CVE-2024-28232
highpriority · track · 30EPSS 0.006 · 49 %ileEUUSEPSS · scored 2026-10-27
Go package IceWhaleTech/CasaOS-UserService provides user management functionalities to CasaOS. The Casa OS Login page has disclosed the username enumeration vulnerability in the login page which was patched in version 0.4.7. This issue in CVE-2024-28232 has been patched in version 0.4.8 but that version has not yet been uploaded to Go's package manager.
cvss
Technical severity, 0–10. One row per scoring source.
base score 0–10 · higher = more severe · hover a vector to decode⚠ sources disagree · medium–high · 6.2–7.5
ssvc
A stakeholder decision — act, attend, or track — from exploitation and impact.
weaknesses
The CWE weakness classes this flaw belongs to.
affected products (5)
Products and version ranges known to be affected.
- Go github.com/IceWhaleTech/CasaOS-UserService< 0.4.8osvUSpkg:golang/github.com/IceWhaleTech/CasaOS-UserService
- Go github.com/IceWhaleTech/CasaOS-UserService0.4.7 → 0.4.8osvUSpkg:golang/github.com/IceWhaleTech/CasaOS-UserService
advisories (2)
Vendor and ecosystem advisories describing this.
- GHSA-hcw2-2r9c-gc6pCasaOS Username Enumeration - Bypass of CVE-2024-247662024-04-01ghsa · osvUS
### Summary The Casa OS Login page has disclosed the username enumeration vulnerability in the login page which was patched in `CasaOS v0.4.7`. ### Details It is observed that the attacker can enumerate the CasaOS username using the application response. If the username is incorrect the application gives the error "**User does not exist**" with success code "**10006**", If the password is incorrect the application gives the error "**User does not exist or password is invalid**" with success code "**10013**". ### PoC 1. If the Username is invalid application gives "User does not exist" with success code "**10006**". 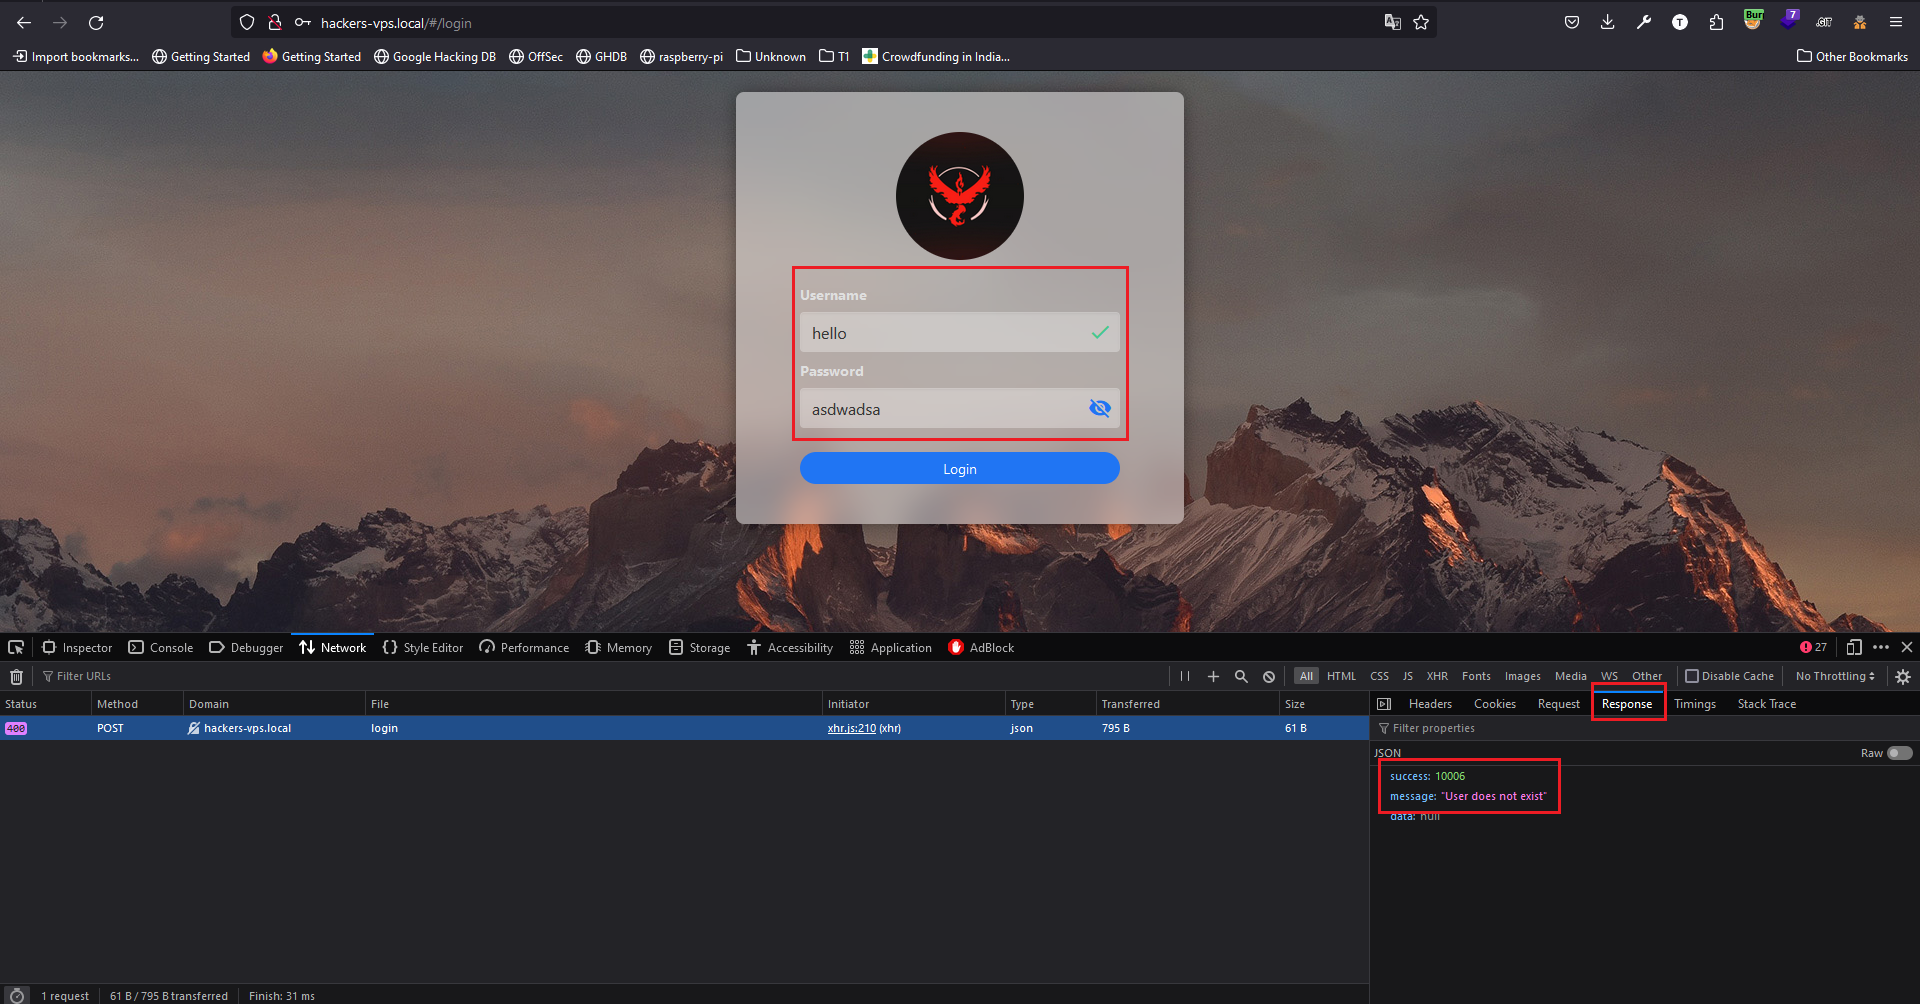 2. If the Password is invalid application gives "**User does not exist or password is invalid**" with success code "**10013**". 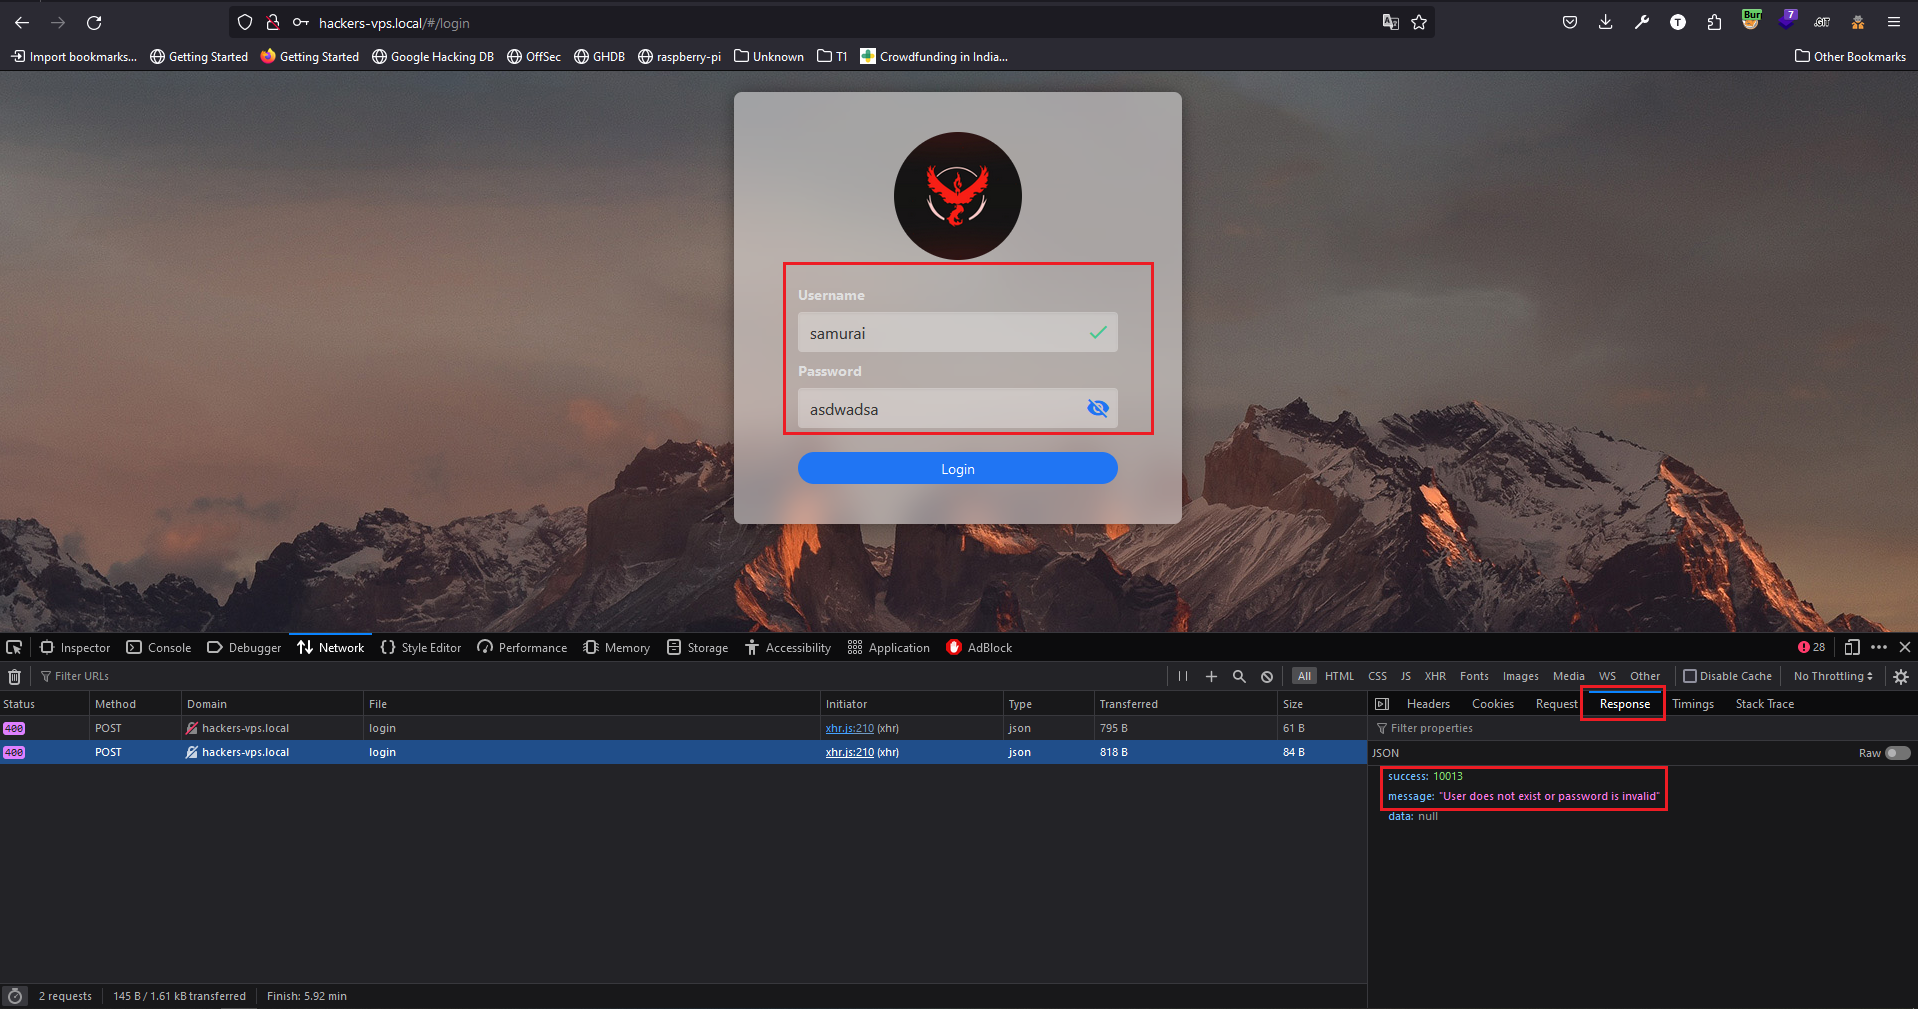 ### Impact Using this error attacker can enumerate the username of CasaOS. ### The logic behind the issue The logic behind the issue If the username is incorrect, then throw an error "**User does not exist**" with success code "**10006**", else throw an error "**User does not exist or password is invalid**" with success code "**10013**". This condition can be vice versa like: If the password is incorrect, then throw an error "**User does not exist or password is invalid**" with success code "**10013**", else throw an error "**User does not exist**" with success code "**10006**". ### Mitigation Since this is the condition we have to implement a single error which can be "**Username/Password is Incorrect!!!**" with single success code.
- GO-2024-2668Login username enumeration in github.com/IceWhaleTech/CasaOS-UserService2024-04-02vendor · osvUS
The Casa OS Login page has a username enumeration vulnerability in the login page that was patched in Casa OS v0.4.7. The issue exists because the application response differs depending on whether the username or password is incorrect, allowing an attacker to enumerate usernames by observing the application response. For example, if the username is incorrect, the application returns "User does not exist" with return code "10006", while if the password is incorrect, it returns "User does not exist or password is invalid" with return code "10013". This allows an attacker to determine if a username exists without knowing the password.
also known as (5)
Other names and identifiers for this entity.
sources
Which sources assert this record, and when.
references (7)
External citations — patches, advisories, analysis.
- https://cxsecurity.com/cveshow/CVE-2024-28232/cnnvd
- https://github.com/IceWhaleTech/CasaOS-UserService/commit/dd927fe1c805e53790f73cfe10c7a4ded3bc5bdbcnnvd
- https://github.com/IceWhaleTech/CasaOS-UserService/security/advisories/GHSA-hcw2-2r9c-gc6pcnnvd
- https://github.com/IceWhaleTech/CasaOS-UserService/commit/dd927fe1c805e53790f73cfe10c7a4ded3bc5bdbenisa_euvd
- https://github.com/IceWhaleTech/CasaOS-UserService/security/advisories/GHSA-hcw2-2r9c-gc6penisa_euvd
- https://github.com/IceWhaleTech/CasaOS-UserService/commit/dd927fe1c805e53790f73cfe10c7a4ded3bc5bdbPatchnvd
- https://github.com/IceWhaleTech/CasaOS-UserService/security/advisories/GHSA-hcw2-2r9c-gc6pExploitVendor Advisorynvd
Attackers weaponise vulnerabilities like this against internet-exposed services. See what is exposed on your perimeter with a free passive scan.
Free scan