CasaOS Username Enumeration - Bypass of CVE-2024-24766
### Summary The Casa OS Login page has disclosed the username enumeration vulnerability in the login page which was patched in `CasaOS v0.4.7`. ### Details It is observed that the attacker can enumerate the CasaOS username using the application response. If the username is incorrect the application gives the error "**User does not exist**" with success code "**10006**", If the password is incorrect the application gives the error "**User does not exist or password is invalid**" with success code "**10013**". ### PoC 1. If the Username is invalid application gives "User does not exist" with success code "**10006**". 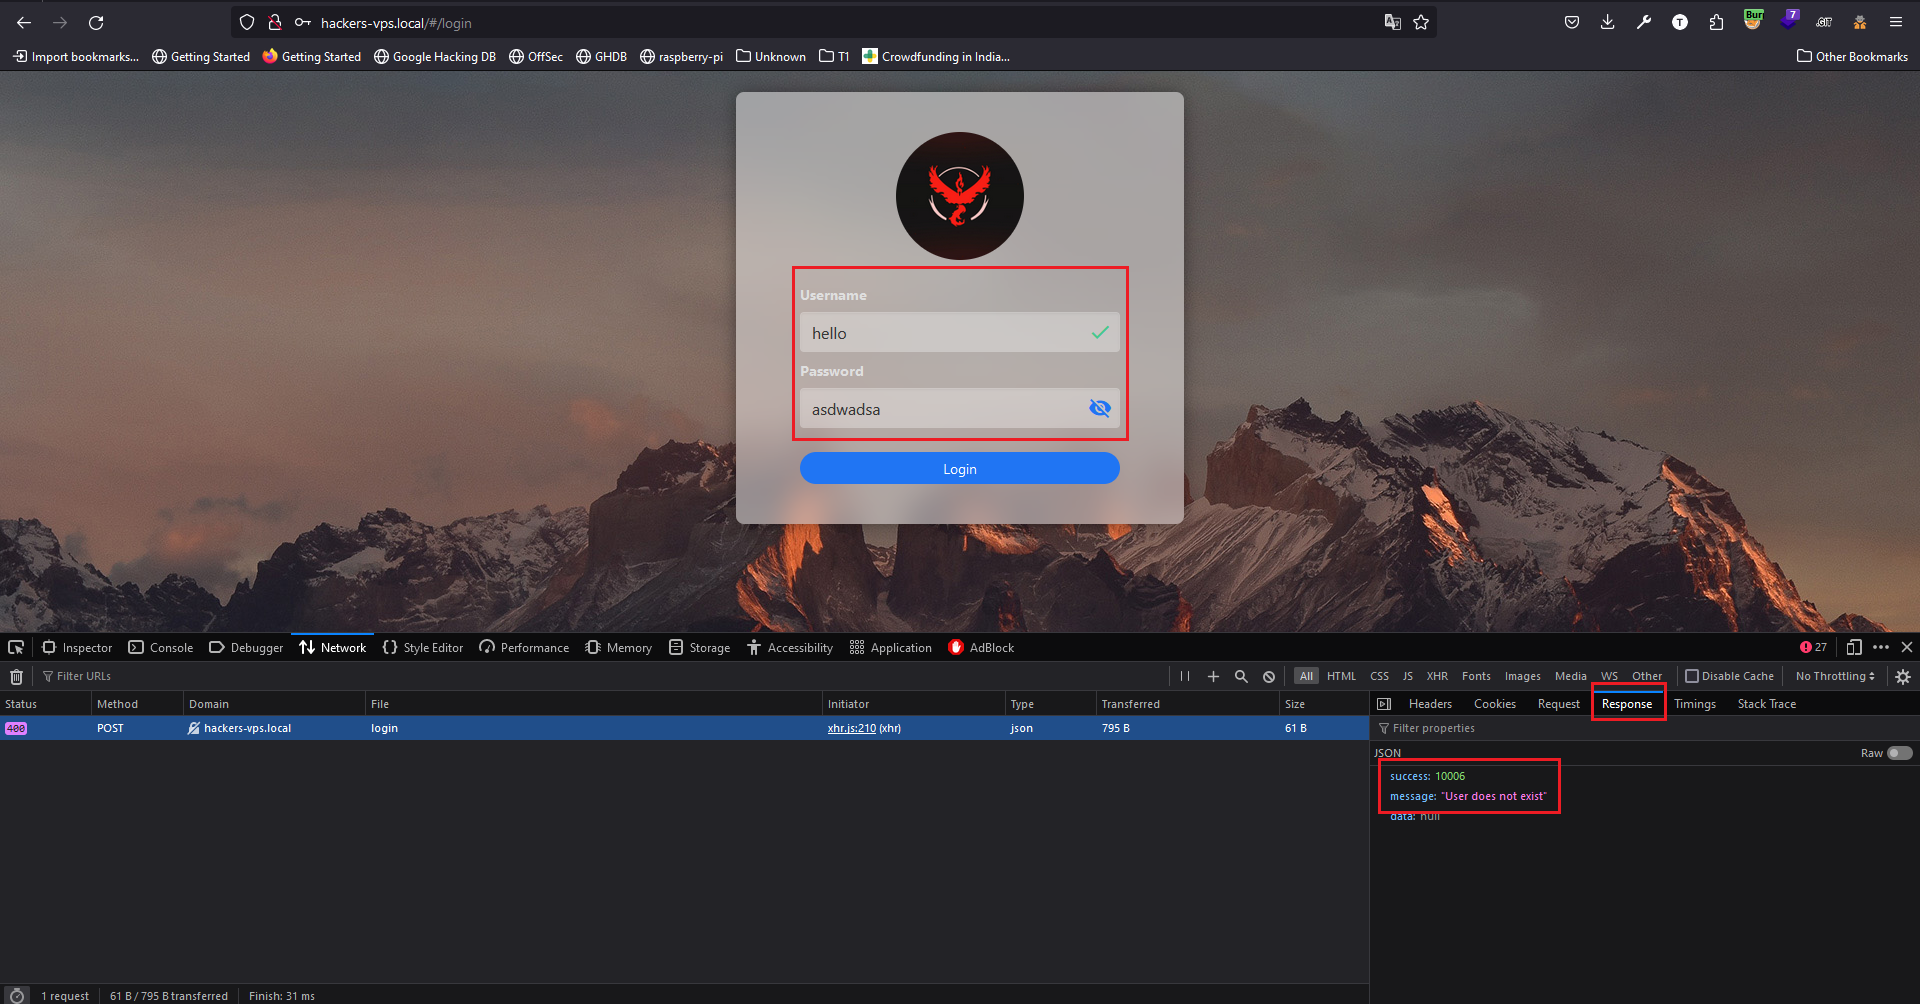 2. If the Password is invalid application gives "**User does not exist or password is invalid**" with success code "**10013**". 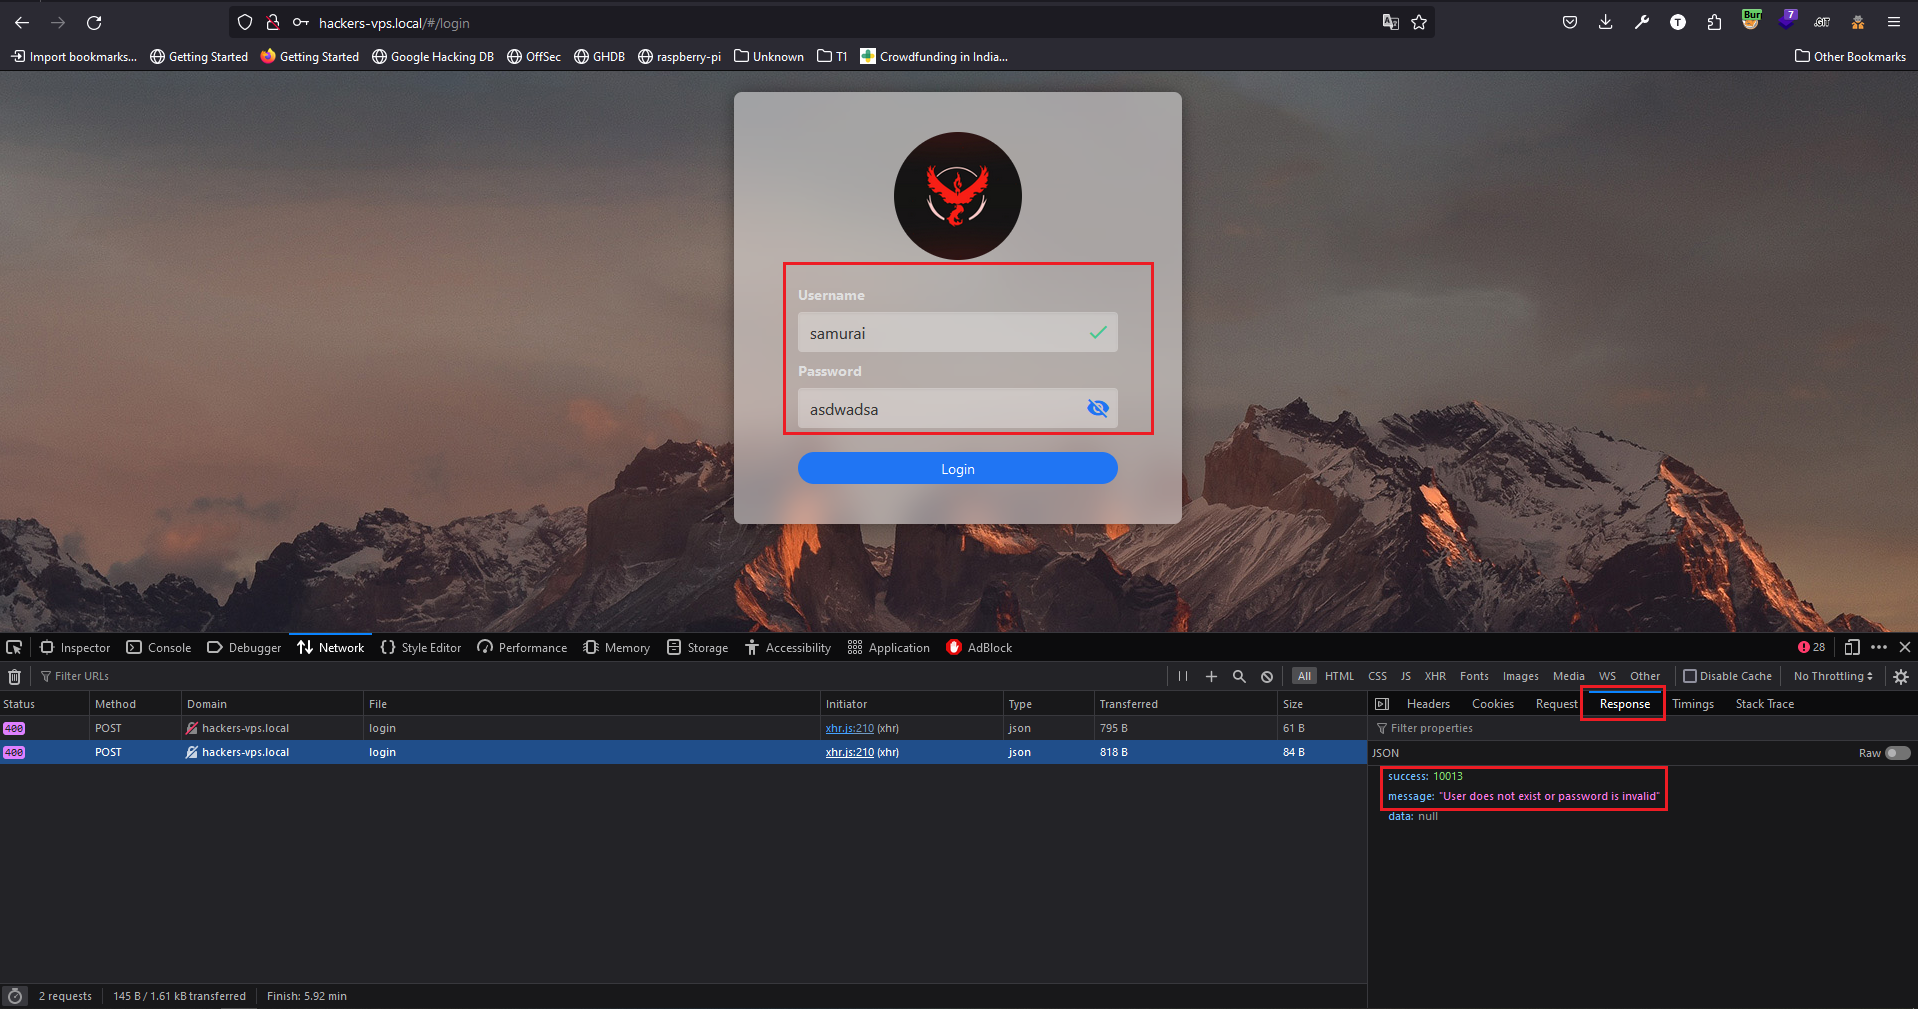 ### Impact Using this error attacker can enumerate the username of CasaOS. ### The logic behind the issue The logic behind the issue If the username is incorrect, then throw an error "**User does not exist**" with success code "**10006**", else throw an error "**User does not exist or password is invalid**" with success code "**10013**". This condition can be vice versa like: If the password is incorrect, then throw an error "**User does not exist or password is invalid**" with success code "**10013**", else throw an error "**User does not exist**" with success code "**10006**". ### Mitigation Since this is the condition we have to implement a single error which can be "**Username/Password is Incorrect!!!**" with single success code.
describes (1)
Related CVEs.
| ID | severity | exploitable | ||
|---|---|---|---|---|
| CVE-2024-28232US | high7.5 | — | ||
Go package IceWhaleTech/CasaOS-UserService provides user management functionalities to CasaOS. The Casa OS Login page has disclosed the username enumeration vulnerability in the lo… | ||||
references
External citations — patches, advisories, analysis.
- https://github.com/IceWhaleTech/CasaOS-UserServicePACKAGE
- https://github.com/IceWhaleTech/CasaOS-UserService/commit/dd927fe1c805e53790f73cfe10c7a4ded3bc5bdbWEB
- https://github.com/IceWhaleTech/CasaOS-UserService/security/advisories/GHSA-hcw2-2r9c-gc6pWEB
- https://nvd.nist.gov/vuln/detail/CVE-2024-28232ADVISORY
Advisories like this name the exposed products attackers go after on your perimeter. See what is exposed on your perimeter with a free passive scan.
Free scan