CVE-2026-52796
lowPriorität · verfolgen · 0EPSS 0.003 · 21. PerzentilDEEUUSEPSS · bewertet 2026-10-27
Gogs is an open source self-hosted Git service. Prior to 0.14.3, specially crafted issue index pattern can cause a panic when rendering, resulting in denial of service. In internal/markup/markup.go, RenderIssueIndexPattern renders the issue index pattern to a link using com.Expand, which is not safe: when the configured pattern contains an opening brace { but no closing brace }, strings.Index(template, "}") returns -1 and the subsequent slice template[:-1] triggers a panic. Once such a pattern is set, any page in the affected repository that contains an issue index reference such as #1 becomes unavailable. This vulnerability is fixed in 0.14.3.
cvss
Technischer Schweregrad, 0–10. Eine Zeile je Quelle.
Basiswert 0–10 · höher = schwerwiegender · Vektor überfahren zum Auflösen
SSVC
Eine Handlungsentscheidung — aus Ausnutzung und Auswirkung.
schwächen
Die CWE-Schwächeklassen, zu denen dies gehört.
betroffene Produkte (5)
Betroffene Produkte und Versionsbereiche.
Advisories (3)
Hersteller- und Ökosystem-Meldungen dazu.
- WID-SEC-W-2026-2013Gogs: Mehrere SchwachstellenDeutsch2026-06-18csaf · cert_bundDE
Ein Angreifer kann mehrere Schwachstellen in Gogs ausnutzen, um erweiterte Berechtigungen zu erlangen, beliebigen Code auszuführen – sogar mit erweiterten Berechtigungen, was zur vollständigen Kontrolle über das System führen kann –, Sicherheitsmaßnahmen zu umgehen, Daten zu manipulieren, Cross-Site-Scripting-Angriffe durchzuführen, Benutzer auf bösartige Websites umzuleiten oder einen Denial-of-Service-Zustand zu verursachen.
- GHSA-4j89-2c4f-44c6Gogs has DoS in rendering issue index pattern2026-06-22ghsa · osvUS
### Summary Special template of issue index pattern may cause panic. ### Details in internal/markup/markup.go ```go link = fmt.Sprintf(`<a href="%s">%s</a>`, com.Expand(metas["format"], metas), m) ``` Issue index pattern is rendered to link with `com.Expand`. However, `com.Expand` is not safe. ```go i = strings.Index(template, "}") if s, ok := match[template[:i]]; ok { ``` when `{` is found but `}` not found, i comes to 1, template[:-1] will be called, and then panicked 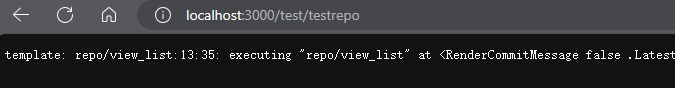 finally, all pages than contains issue index are unavailable. ### PoC 1. set issue index pattern as follow 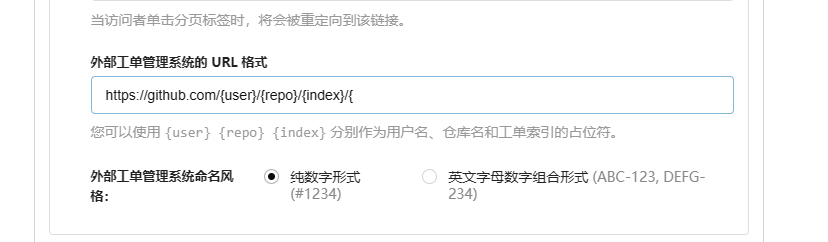 2. add a commit which point to an issue in its msg 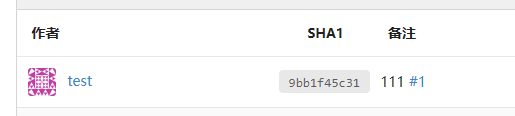 using `#1` above ### Impact DoS that cause part of pages of the specify repo unavailable.
- GO-2026-5124Gogs has DoS in rendering issue index pattern in gogs.io/gogs2026-06-25vendor · osvUS
Gogs has DoS in rendering issue index pattern in gogs.io/gogs. NOTE: The source advisory for this report contains additional versions that could not be automatically mapped to standard Go module versions. (If this is causing false-positive reports from vulnerability scanners, please suggest an edit to the report.) The additional affected modules and versions are: gogs.io/gogs before v0.14.3.
auch bekannt als (5)
Weitere Namen und Kennungen dieser Entität.
quellen
Welche Quellen diesen Datensatz belegen und wann.
Referenzen (3)
Externe Belege — Patches, Meldungen, Analysen.
Angreifer nutzen Schwachstellen wie diese gegen im Internet exponierte Dienste aus. Sehen Sie mit einem kostenlosen Passiv-Scan, was exponiert ist.
Kostenloser Scan