Gogs has DoS in rendering issue index pattern
### Summary Special template of issue index pattern may cause panic. ### Details in internal/markup/markup.go ```go link = fmt.Sprintf(`<a href="%s">%s</a>`, com.Expand(metas["format"], metas), m) ``` Issue index pattern is rendered to link with `com.Expand`. However, `com.Expand` is not safe. ```go i = strings.Index(template, "}") if s, ok := match[template[:i]]; ok { ``` when `{` is found but `}` not found, i comes to 1, template[:-1] will be called, and then panicked 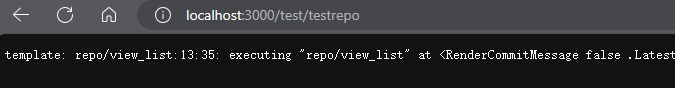 finally, all pages than contains issue index are unavailable. ### PoC 1. set issue index pattern as follow 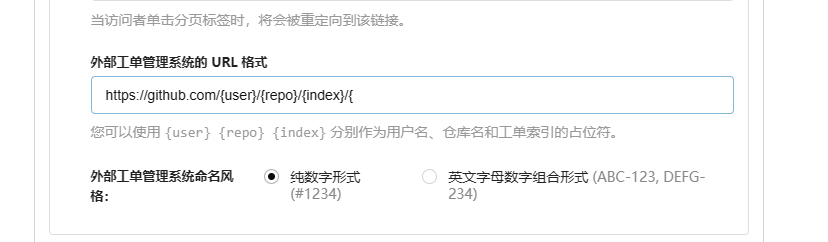 2. add a commit which point to an issue in its msg 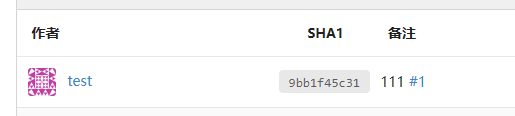 using `#1` above ### Impact DoS that cause part of pages of the specify repo unavailable.
beschreibt (1)
Zugehörige CVEs.
| ID | Schweregrad | ausnutzbar | ||
|---|---|---|---|---|
| CVE-2026-52796US | — | — | ||
Gogs is an open source self-hosted Git service. Prior to 0.14.3, specially crafted issue index pattern can cause a panic when rendering, resulting in denial of service. In internal… | ||||
Referenzen
Externe Belege — Patches, Meldungen, Analysen.
- https://github.com/gogs/gogsPACKAGE
- https://github.com/gogs/gogs/commit/0529d95fc39f2b6d2997b19a2a12e24522684722WEB
- https://github.com/gogs/gogs/pull/8312WEB
- https://github.com/gogs/gogs/releases/tag/v0.14.3WEB
- https://github.com/gogs/gogs/security/advisories/GHSA-4j89-2c4f-44c6WEB
- https://nvd.nist.gov/vuln/detail/CVE-2026-52796ADVISORY
Advisories wie diese benennen die exponierten Produkte, die Angreifer auf Ihrer Angriffsfläche ins Visier nehmen. Sehen Sie mit einem kostenlosen Passiv-Scan, was exponiert ist.
Kostenloser Scan