CVE-2024-29179
mediumpriority · track · 19EPSS 0.005 · 43 %ileEURUUSEPSS · scored 2026-10-27
phpMyFAQ is an open source FAQ web application for PHP 8.1+ and MySQL, PostgreSQL and other databases. An attacker with admin privileges can upload an attachment containing JS code without extension and the application will render it as HTML which allows for XSS attacks.
cvss
Technical severity, 0–10. One row per scoring source.
base score 0–10 · higher = more severe · hover a vector to decode
ssvc
A stakeholder decision — act, attend, or track — from exploitation and impact.
weaknesses
The CWE weakness classes this flaw belongs to.
affected products (5)
Products and version ranges known to be affected.
advisories (1)
Vendor and ecosystem advisories describing this.
- GHSA-hm8r-95g3-5hj9phpMyFAQ Stored Cross-site Scripting at File Attachments2024-03-25ghsa · osvUS
### Summary An attacker with admin privileges can upload an attachment containing JS code without extension and the application will render it as HTML which allows for XSS attacks. ### Details When attachments are uploaded without an extension, the application renders it as HTML by default. Therefore allowing attackers to upload .html files containing javascript code to perform XSS attacks. The direct file path to the uploaded attachment is also easily obtainable as it is made up of substrings of the file's MD5 hashes. ### PoC 1. Admin users can upload attachments containing XSS payloads in files without extensions to bypass the .html extension check. 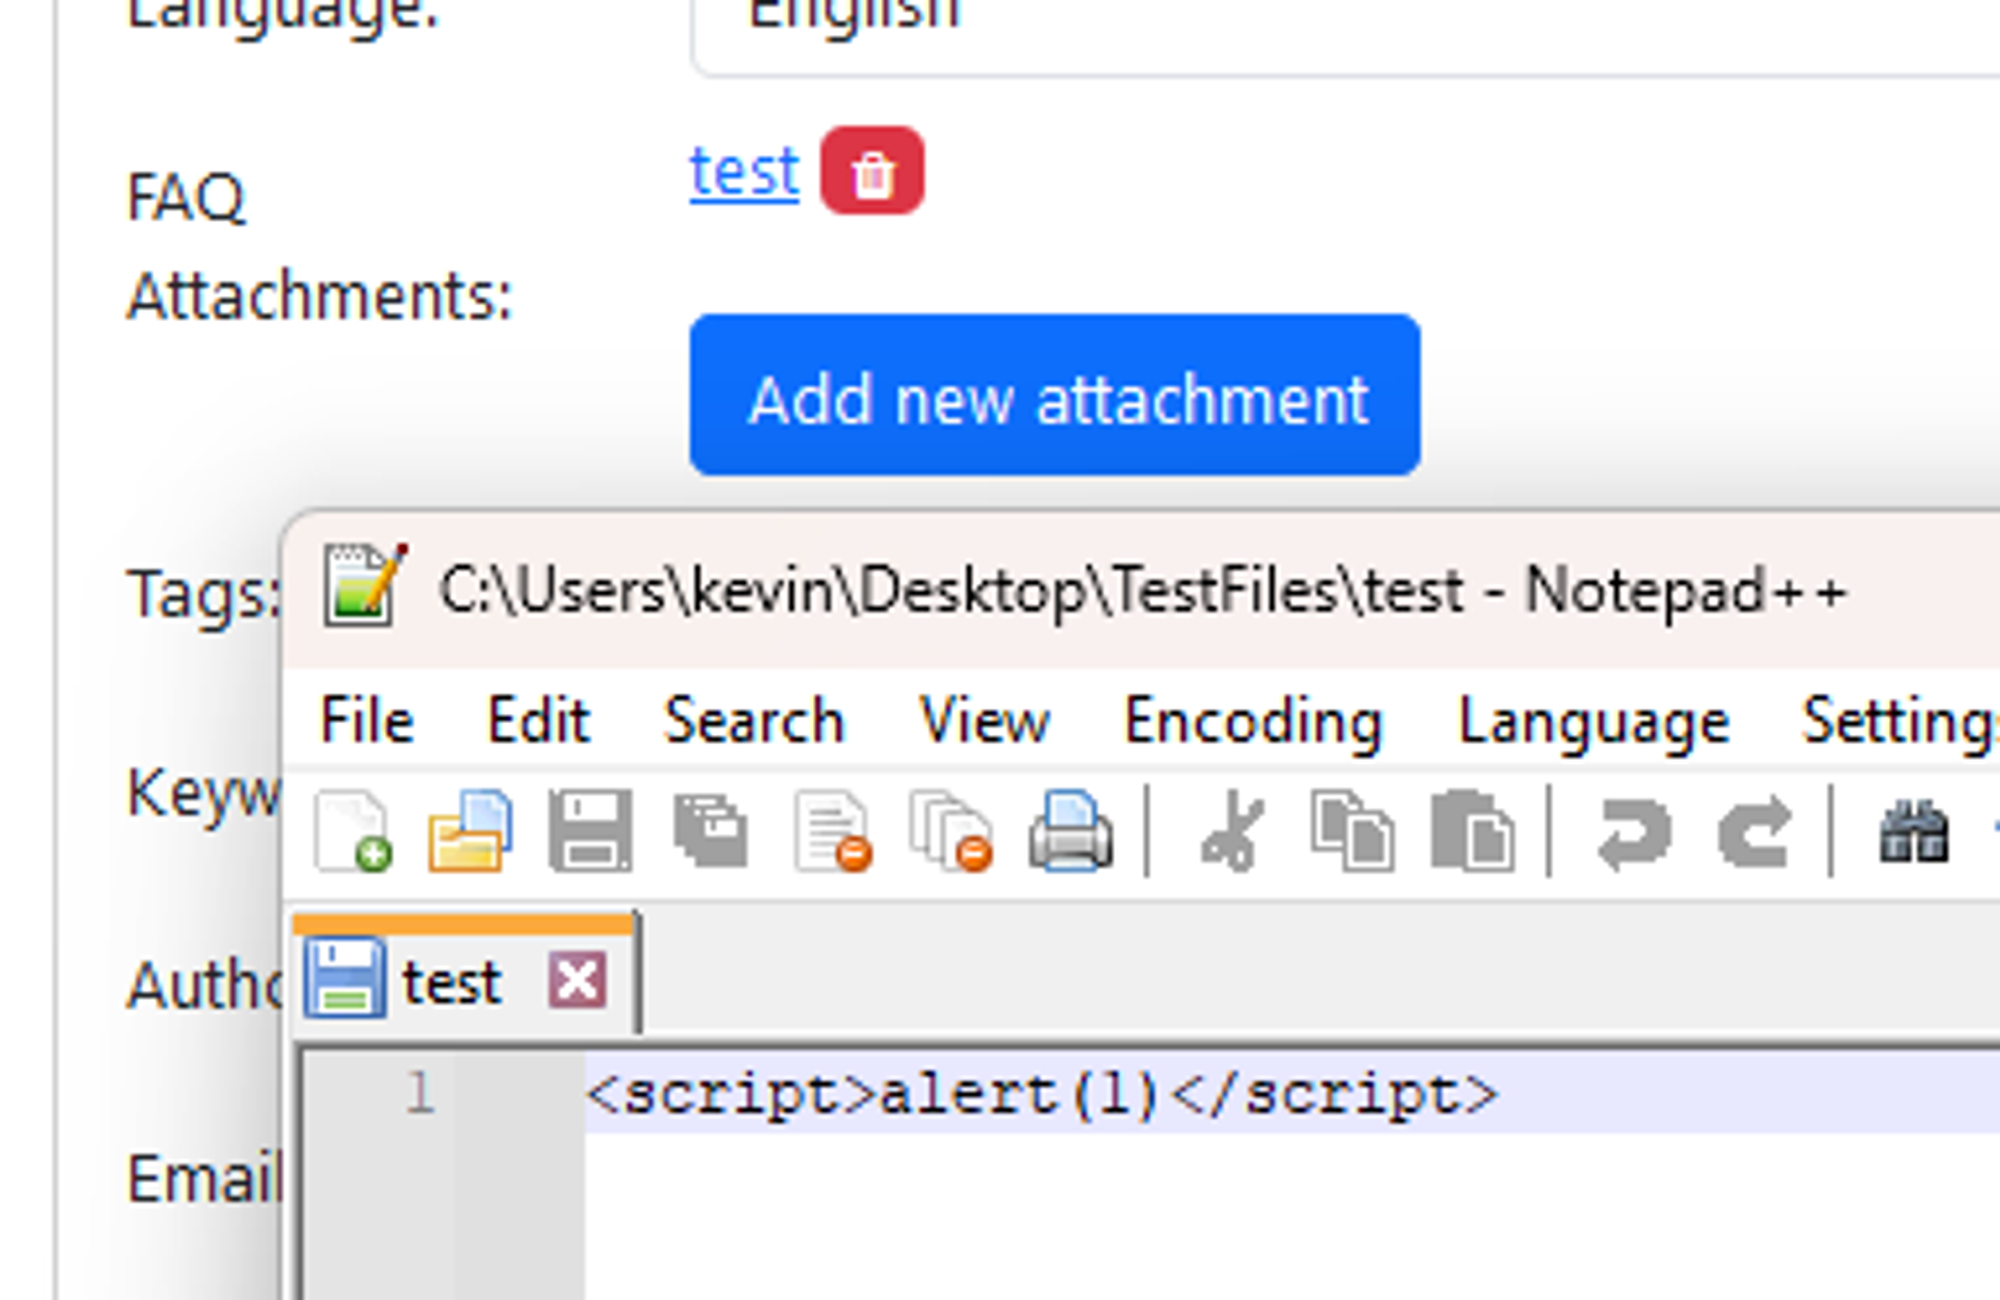 2. Since the path of the uploaded file is built entirely on the file’s MD5 hash and the attachment directory, it is possible for an attacker to know the direct path of the uploaded file. E.g file MD5 hash: 38fff51cb7248a06d6142c6bdf846831 URL will be: http://127.0.0.1/phpmyfaq/attachments/38fff/51cb7/248a0/6d6142c6bdf846831 - /attachments - /38fff (first 5 chars of MD5 hash) - /51cb7 (next 5 chars of MD5 hash) - /248a0 (next 5 chars of MD5 hash) - /6d6142c6bdf846831 (remaining chars of MD5 hash) 3. Even though the attachment was uploaded without a file extension, it is still rendered as .html, hence triggering the XSS payload. 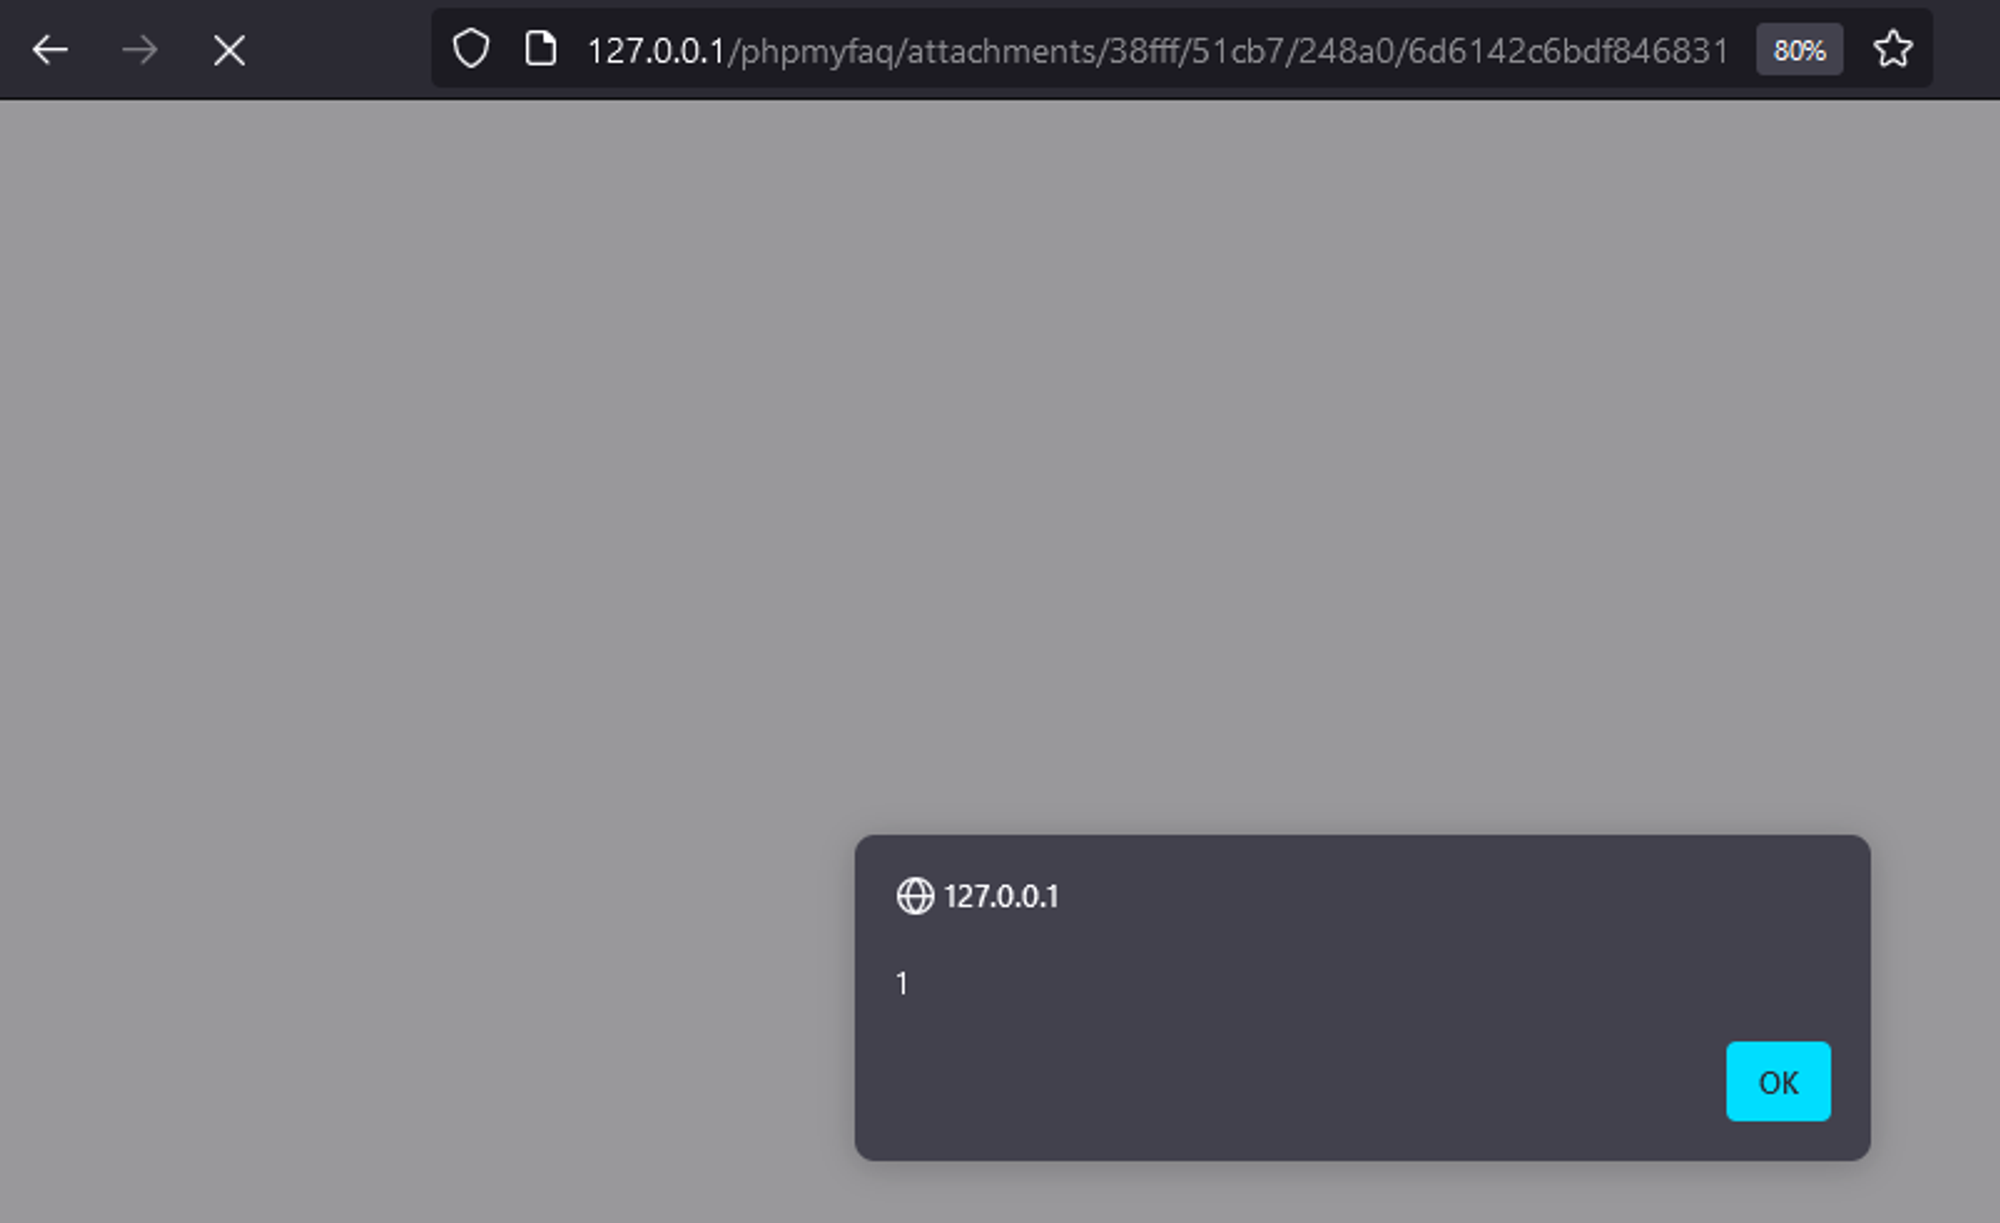 ### Impact This allows an attacker to execute arbitrary client side JavaScript within the context of another user's phpMyFAQ session.
also known as (4)
Other names and identifiers for this entity.
sources
Which sources assert this record, and when.
references (4)
External citations — patches, advisories, analysis.
- https://cxsecurity.com/cveshow/CVE-2024-29179/cnnvd
- https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-hm8r-95g3-5hj9cnnvd
- https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-hm8r-95g3-5hj9enisa_euvd
- https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-hm8r-95g3-5hj9ExploitVendor Advisorynvd
Attackers weaponise vulnerabilities like this against internet-exposed services. See what is exposed on your perimeter with a free passive scan.
Free scan