CVE-2024-28106
mediumpriority · track · 22EPSS 0.005 · 45 %ileEURUUSEPSS · scored 2026-10-27
phpMyFAQ is an open source FAQ web application for PHP 8.1+ and MySQL, PostgreSQL and other databases. By manipulating the news parameter in a POST request, an attacker can inject malicious JavaScript code. Upon browsing to the compromised news page, the XSS payload triggers. This vulnerability is fixed in 3.2.6.
cvss
Technical severity, 0–10. One row per scoring source.
base score 0–10 · higher = more severe · hover a vector to decode
ssvc
A stakeholder decision — act, attend, or track — from exploitation and impact.
weaknesses
The CWE weakness classes this flaw belongs to.
affected products (5)
Products and version ranges known to be affected.
advisories (1)
Vendor and ecosystem advisories describing this.
- GHSA-6p68-36m6-392rphpMyFAQ Stored Cross-site Scripting at FAQ News Content2024-03-25ghsa · osvUS
### Summary By manipulating the news parameter in a POST request, an attacker can inject malicious JavaScript code. Upon browsing to the compromised news page, the XSS payload triggers. ### PoC 1. Edit a FAQ news, intercept the request and modify the `news` parameter in the POST body with the following payload: `%3cscript%3ealert('xssContent')%3c%2fscript%3e` 2. Browse to the particular news page and the XSS should pop up. 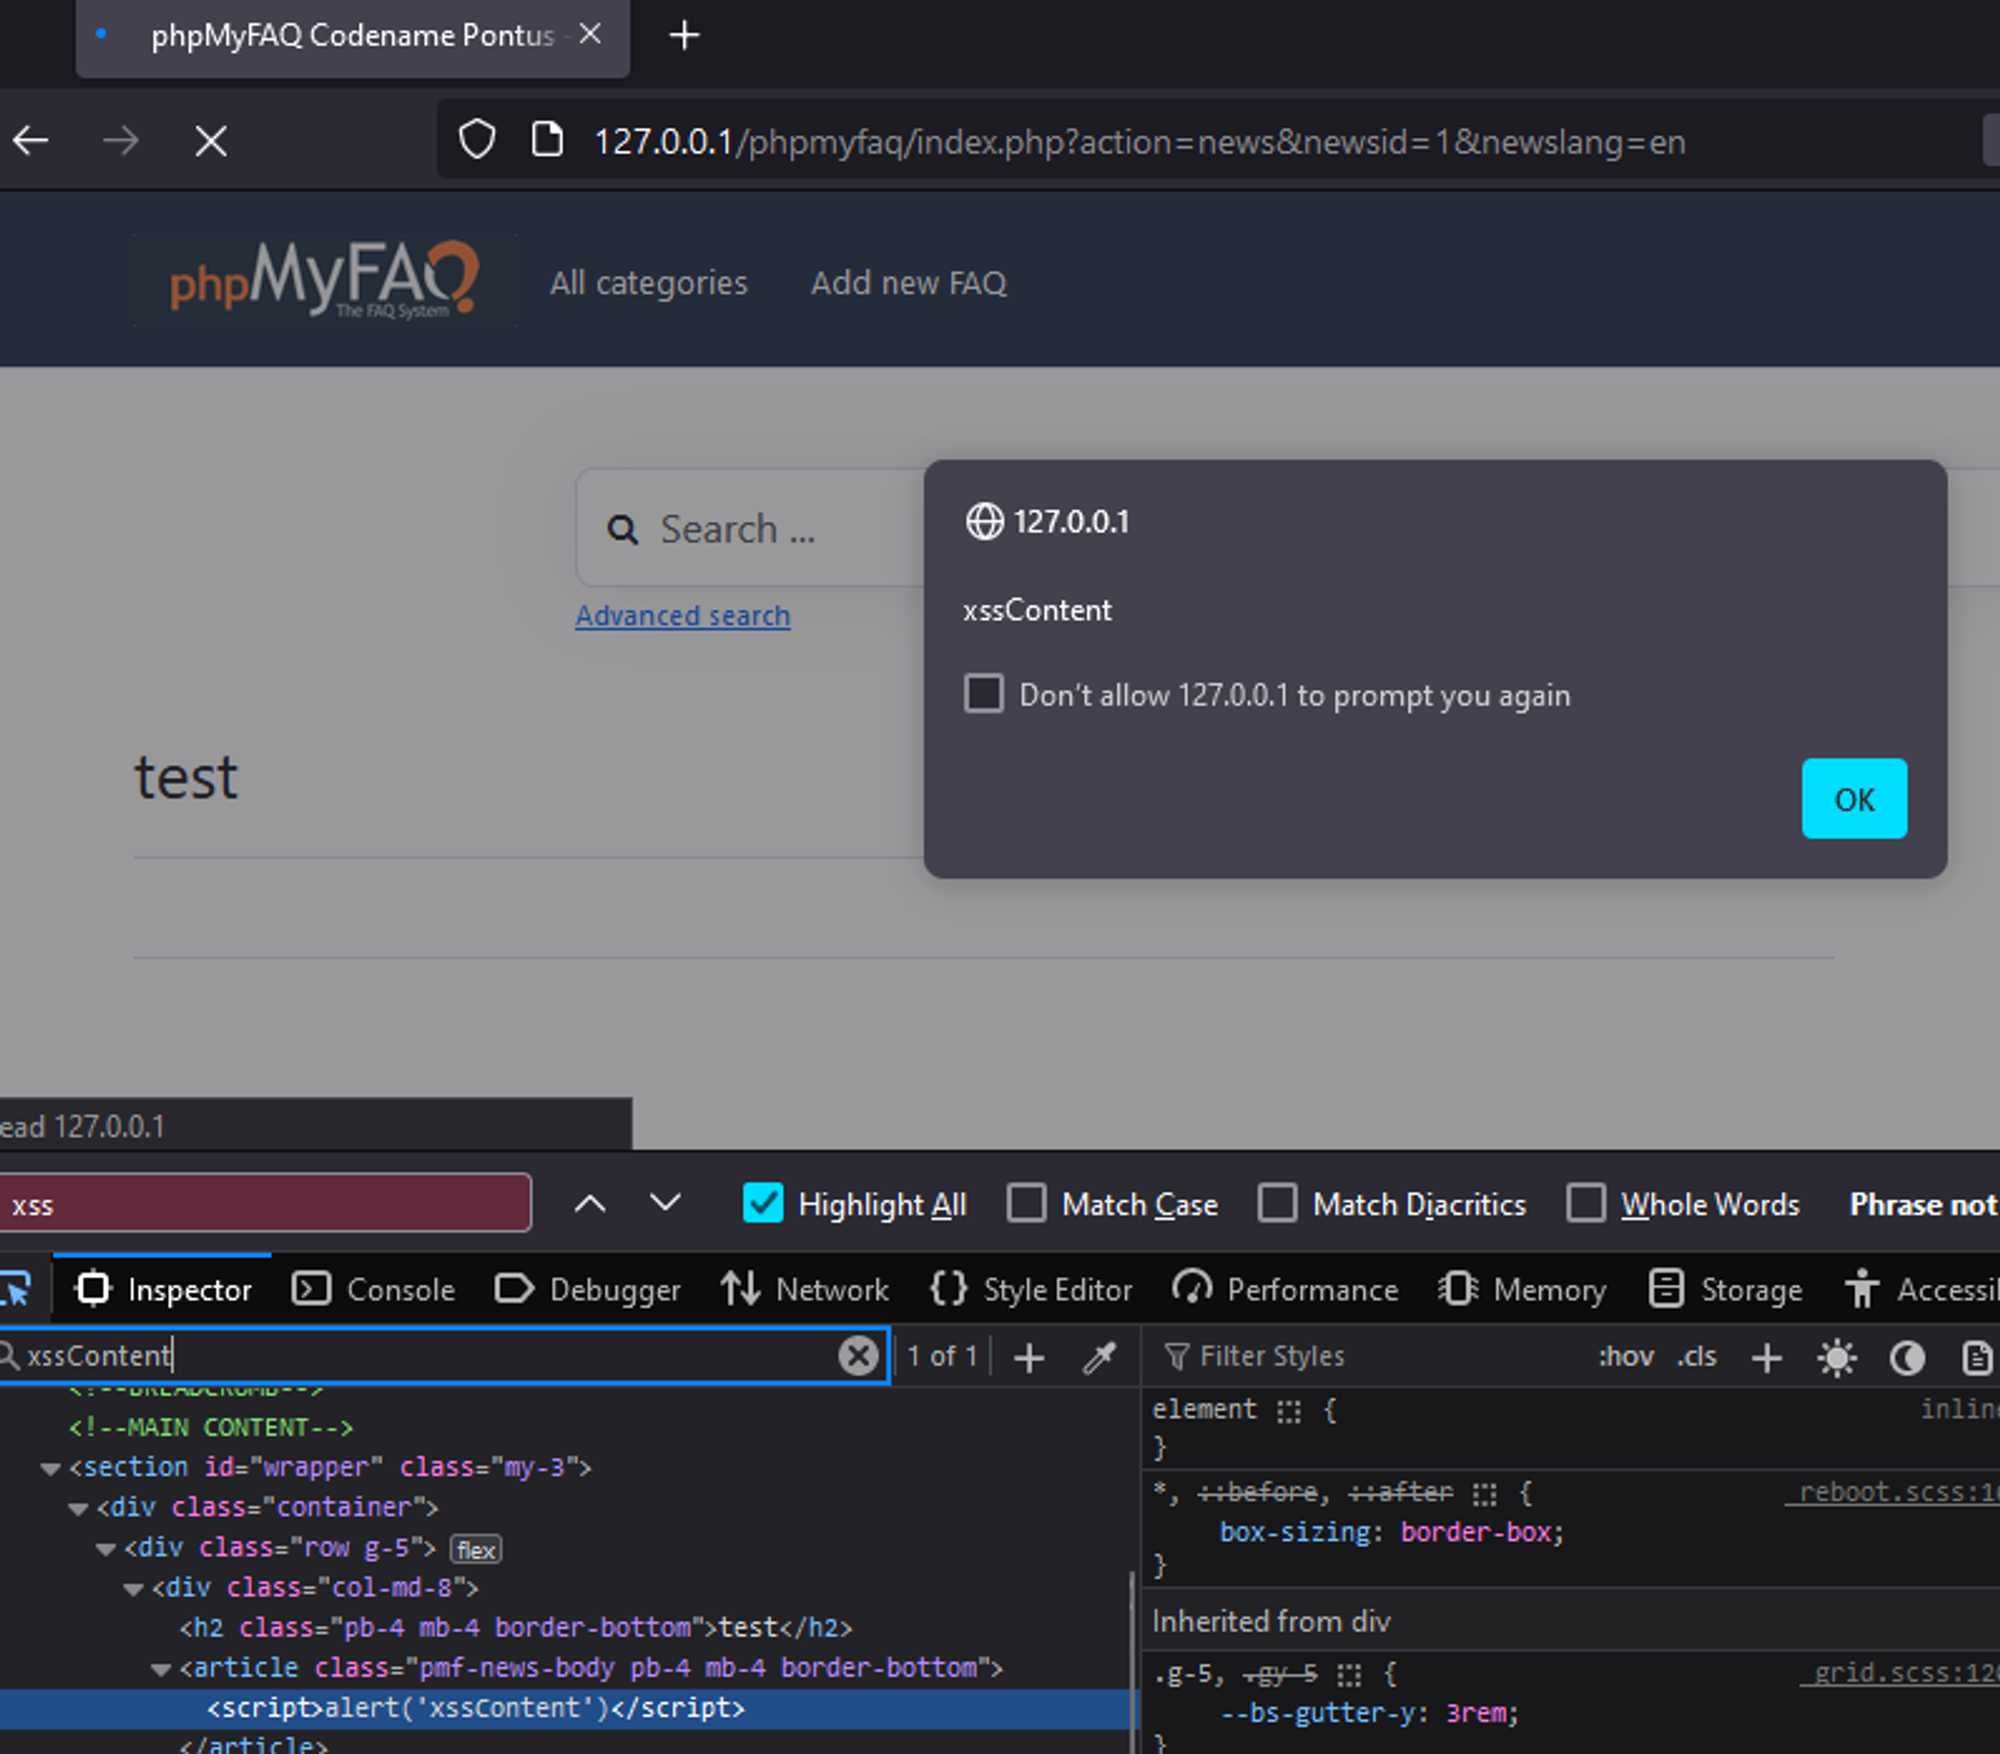 ### Impact This allows an attacker to execute arbitrary client side JavaScript within the context of another user's phpMyFAQ session
also known as (4)
Other names and identifiers for this entity.
sources
Which sources assert this record, and when.
references (7)
External citations — patches, advisories, analysis.
- https://cxsecurity.com/cveshow/CVE-2024-28106/cnnvd
- https://github.com/thorsten/phpMyFAQ/commit/c94b3deadd87789389e1fad162bc3dd595c0e15acnnvd
- https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-6p68-36m6-392rcnnvd
- https://github.com/thorsten/phpMyFAQ/commit/c94b3deadd87789389e1fad162bc3dd595c0e15aenisa_euvd
- https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-6p68-36m6-392renisa_euvd
- https://github.com/thorsten/phpMyFAQ/commit/c94b3deadd87789389e1fad162bc3dd595c0e15aPatchnvd
- https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-6p68-36m6-392rExploitVendor Advisorynvd
Attackers weaponise vulnerabilities like this against internet-exposed services. See what is exposed on your perimeter with a free passive scan.
Free scan