CVE-2024-27288
lowpriority · track · 12OT risk · elevatedEPSS 0.005 · 41 %ileEUUSEPSS · scored 2026-10-27
1Panel is an open source Linux server operation and maintenance management panel. Prior to version 1.10.1-lts, users can use Burp to obtain unauthorized access to the console page. The vulnerability has been fixed in v1.10.1-lts. There are no known workarounds.
cvss
Technical severity, 0–10. One row per scoring source.
base score 0–10 · higher = more severe · hover a vector to decode⚠ sources disagree · low–medium · 2.9–6.3
ssvc
A stakeholder decision — act, attend, or track — from exploitation and impact.
weaknesses
The CWE weakness classes this flaw belongs to.
affected products (4)
Products and version ranges known to be affected.
advisories (2)
Vendor and ecosystem advisories describing this.
- GHSA-26w3-q4j8-4xjp1Panel open source panel project has an unauthorized vulnerability.2024-03-06ghsa · osvUS
### Impact The steps are as follows: 1. Access https://IP:PORT/ in the browser, which prompts the user to access with a secure entry point. 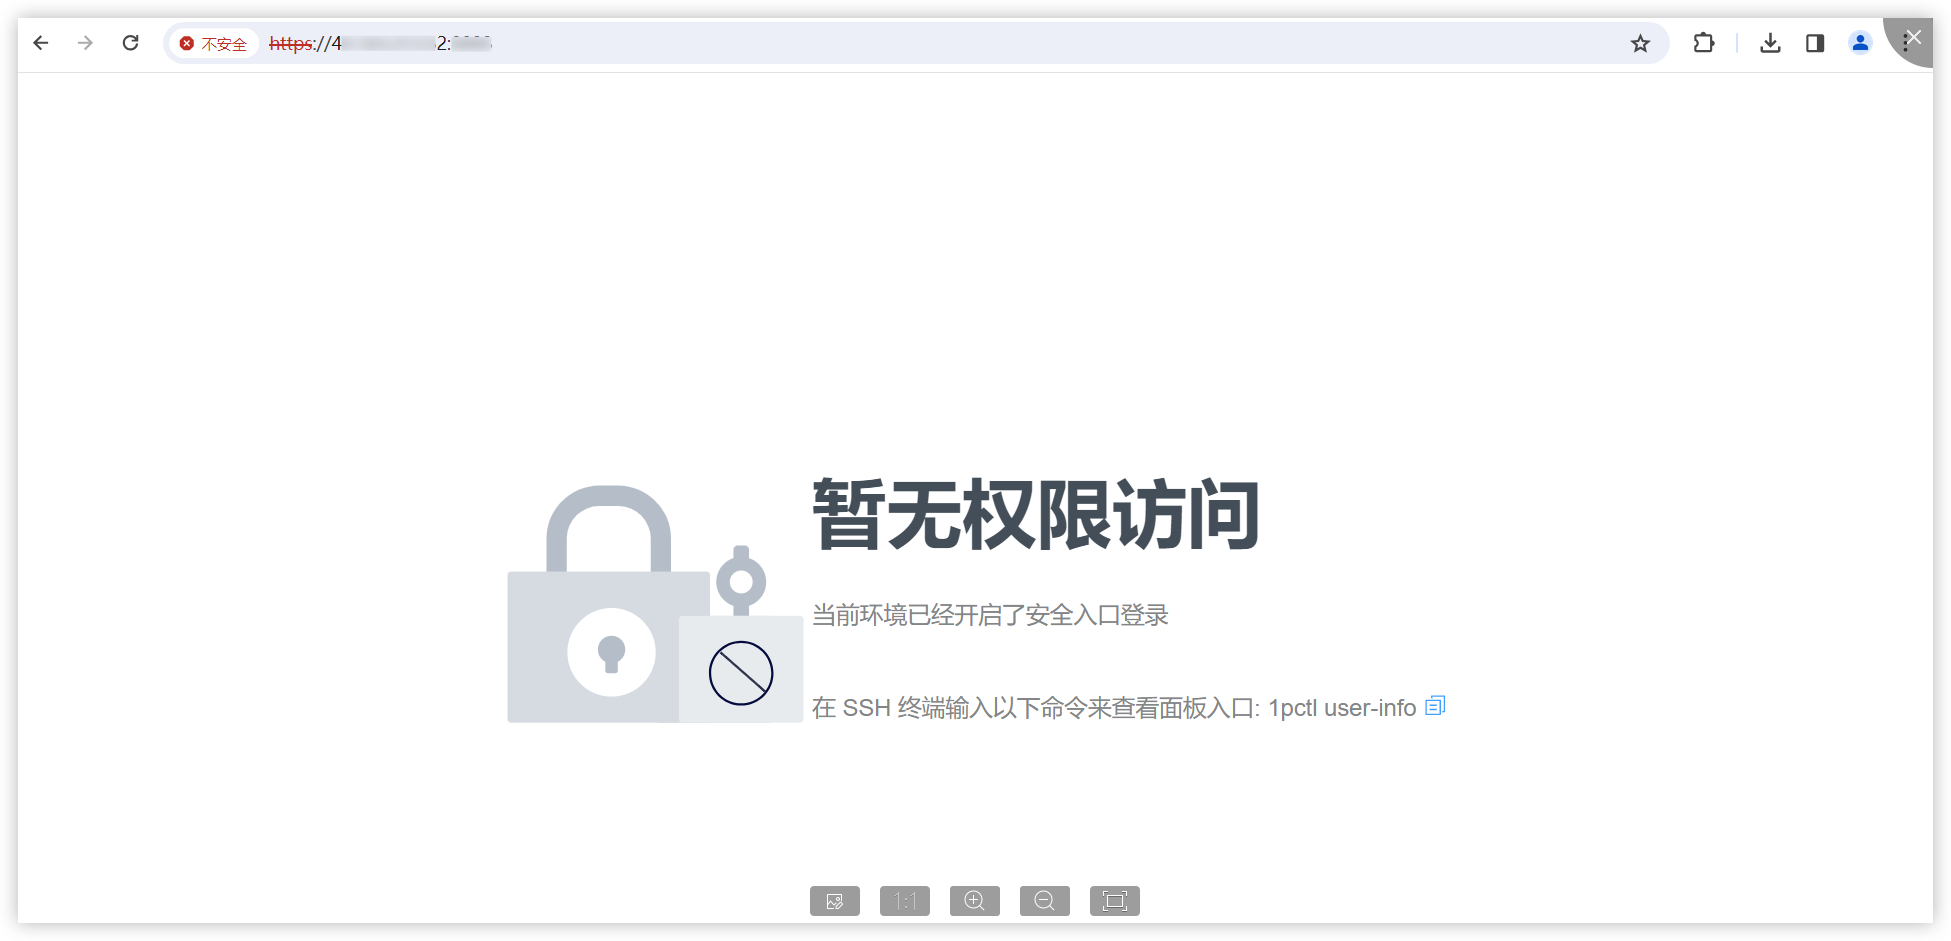 2. Use Burp to intercept: 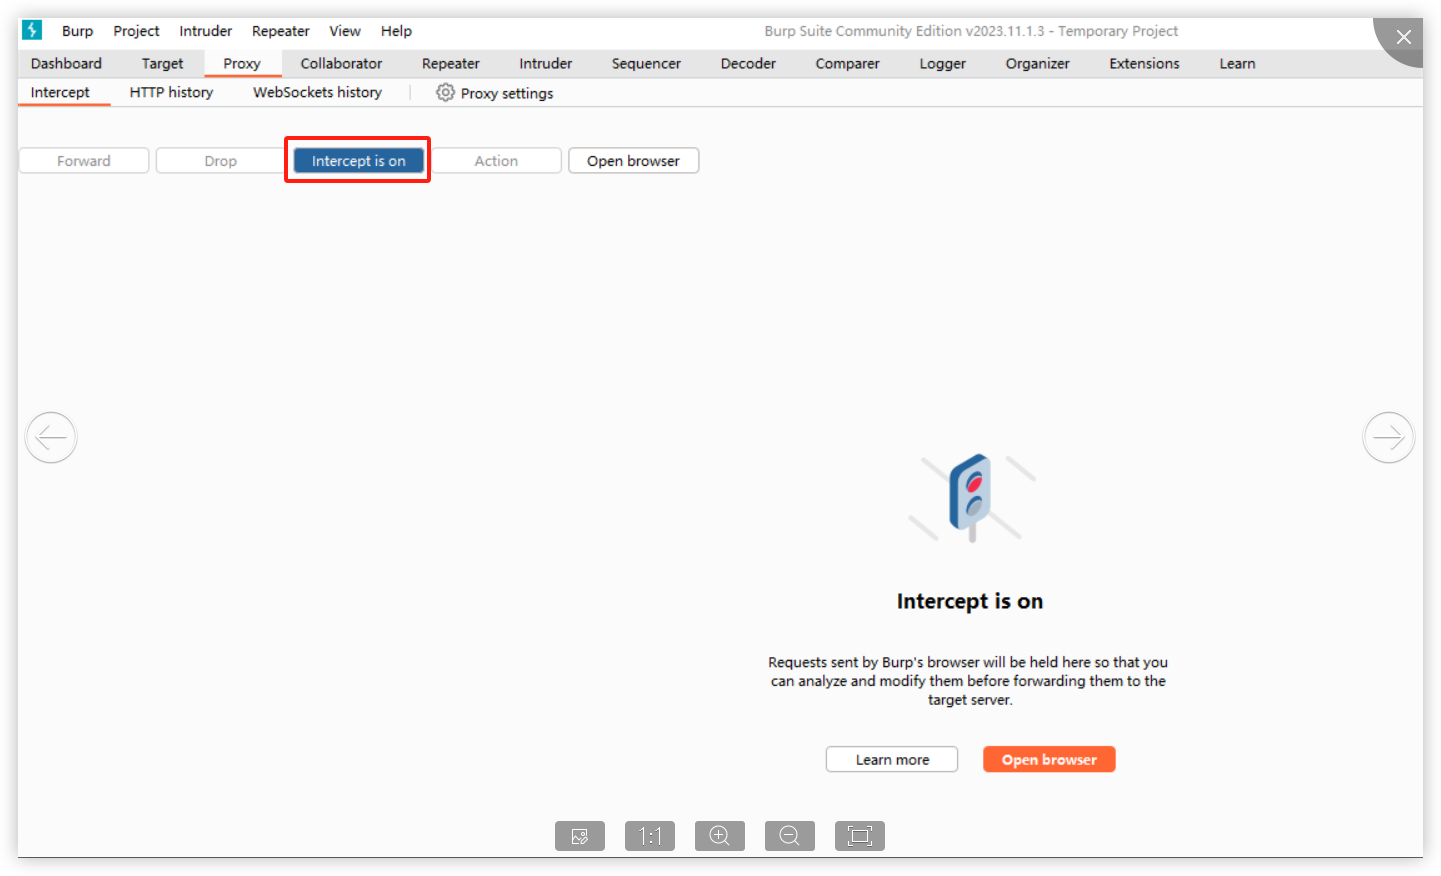 When opening the browser and entering the URL (allowing the first intercepted packet through Burp), the following is displayed: 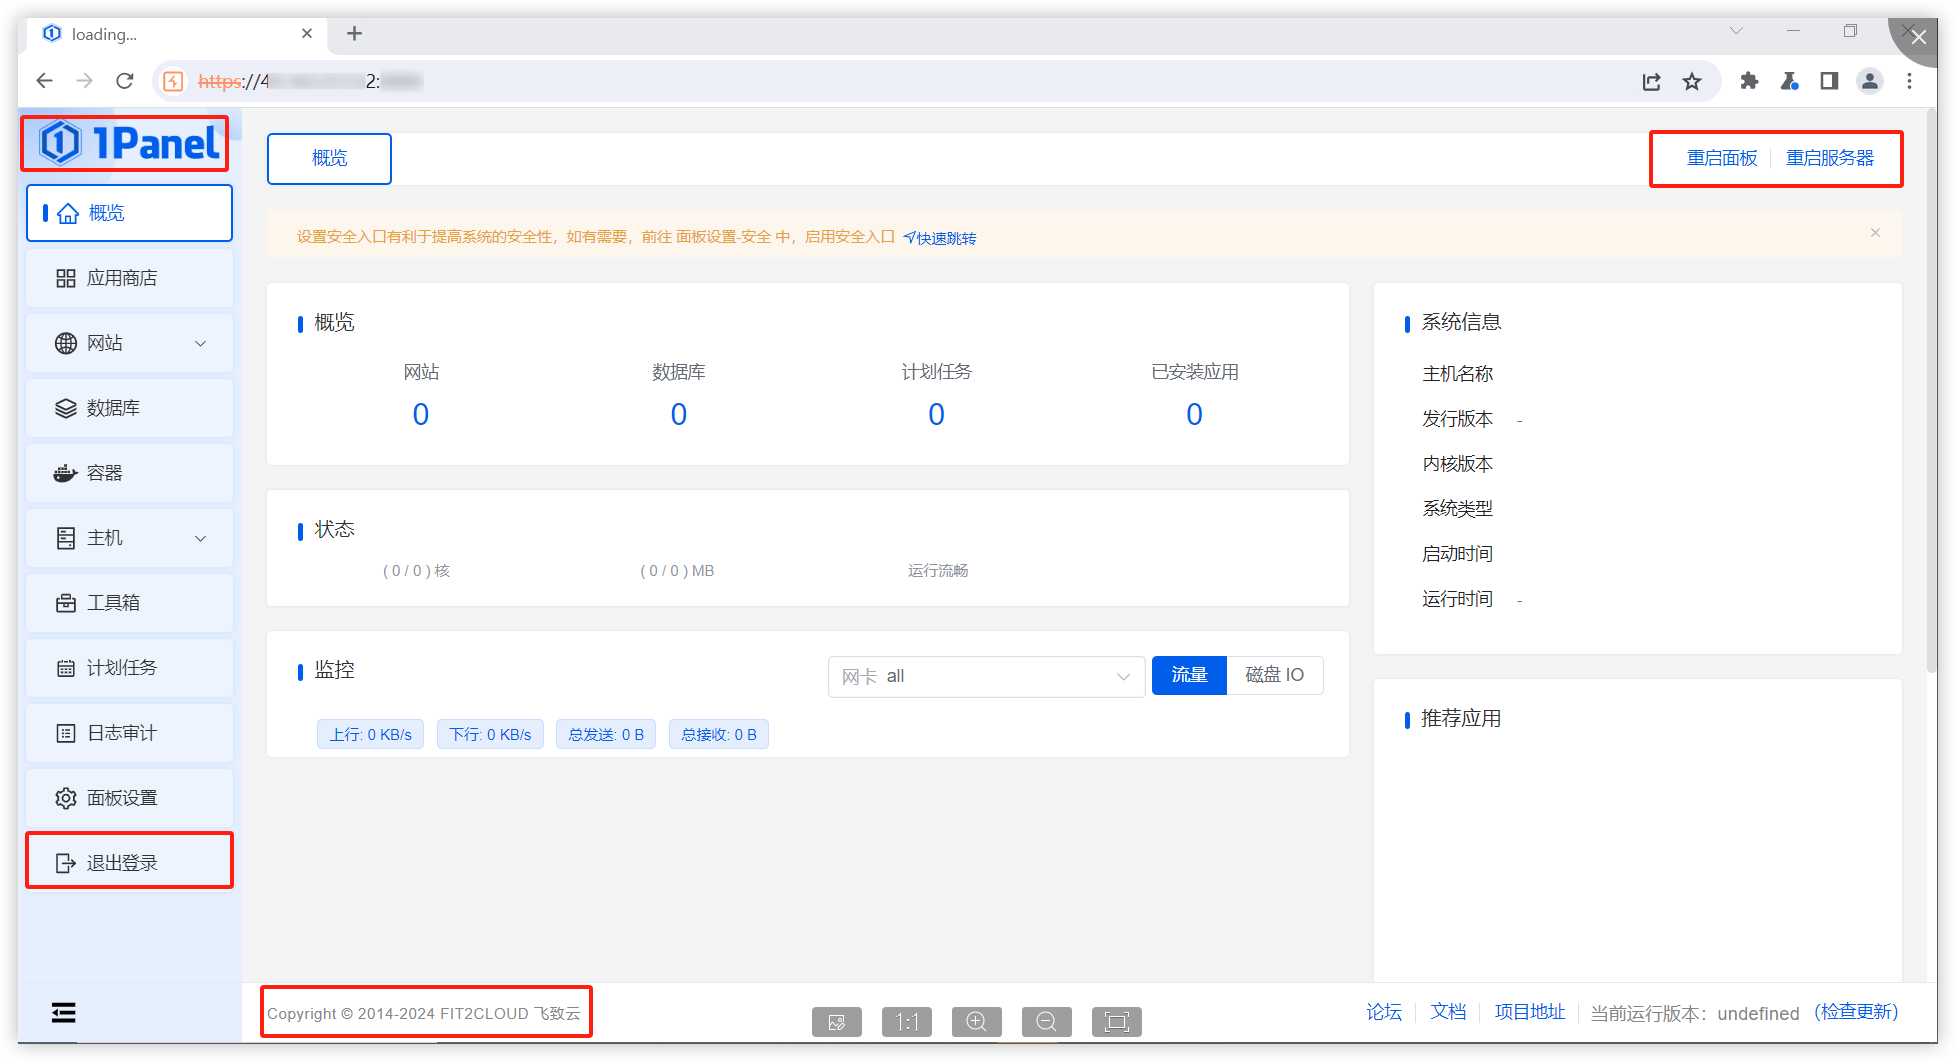 It is found that in this situation, we can access the console page (although no data is returned and no modification operations can be performed)." Affected versions: <= 1.10.0-lts ### Patches The vulnerability has been fixed in v1.10.1-lts. ### Workarounds It is recommended to upgrade the version to 1.10.1-lts. ### References If you have any questions or comments about this advisory: Open an issue in https://github.com/1Panel-dev/1Panel Email us at wanghe@fit2cloud.com
- GO-2024-2613Unauthorized Console access in github.com/1Panel-dev/1Panel2024-03-14vendor · osvUS
If the user attempts to access a secure entry point and intercepts with Burp, they can get access to the console page. This access does not return data nor allow modification operations.
also known as (5)
Other names and identifiers for this entity.
sources
Which sources assert this record, and when.
references (7)
External citations — patches, advisories, analysis.
- https://cxsecurity.com/cveshow/CVE-2024-27288/cnnvd
- https://github.com/1Panel-dev/1Panel/releases/tag/v1.10.1-ltscnnvd
- https://github.com/1Panel-dev/1Panel/security/advisories/GHSA-26w3-q4j8-4xjpcnnvd
- https://github.com/1Panel-dev/1Panel/releases/tag/v1.10.1-ltsenisa_euvd
- https://github.com/1Panel-dev/1Panel/security/advisories/GHSA-26w3-q4j8-4xjpenisa_euvd
- https://github.com/1Panel-dev/1Panel/releases/tag/v1.10.1-ltsRelease Notesnvd
- https://github.com/1Panel-dev/1Panel/security/advisories/GHSA-26w3-q4j8-4xjpExploitVendor Advisorynvd
Attackers weaponise vulnerabilities like this against internet-exposed services. See what is exposed on your perimeter with a free passive scan.
Free scan