CVE-2023-49276
mediumpriority · track · 24EPSS 0.005 · 42 %ileEUUSEPSS · scored 2026-10-28
Uptime Kuma is an open source self-hosted monitoring tool. In affected versions the Google Analytics element in vulnerable to Attribute Injection leading to Cross-Site-Scripting (XSS). Since the custom status interface can set an independent Google Analytics ID and the template has not been sanitized, there is an attribute injection vulnerability here, which can lead to XSS attacks. This vulnerability has been addressed in commit `f28dccf4e` which is included in release version 1.23.7. Users are advised to upgrade. There are no known workarounds for this vulnerability.
cvss
Technical severity, 0–10. One row per scoring source.
base score 0–10 · higher = more severe · hover a vector to decode
weaknesses
The CWE weakness classes this flaw belongs to.
affected products (3)
Products and version ranges known to be affected.
advisories (1)
Vendor and ecosystem advisories describing this.
- GHSA-v4v2-8h88-65qjAttribute Injection leading to XSS(Cross-Site-Scripting)2023-11-24ghsa · osvUS
### Summary Google Analytics element Attribute Injection leading to XSS ### Details Since the custom status interface can set an independent Google Analytics ID and the template has not been sanitized, there is an attribute injection vulnerability here, which can lead to XSS attacks. 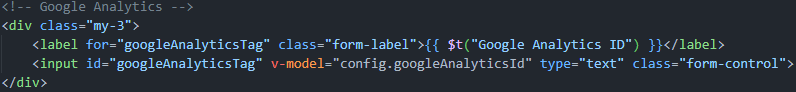 ### PoC 1. Run the latest version of the louislam/uptime-kuma container and initialize the account password. 2. Create a new status page. 3. Edit the status page and change the Google Analytics ID to following payload(it only works for firefox. Any attribute can be injected, but this seems the most intuitive): ``` 123123" onafterscriptexecute=alert(window.name+1),eval(window.name) a="x ``` 4. Click Save and return to the interface. XSS occurs. screenshots:  
also known as (3)
Other names and identifiers for this entity.
sources
Which sources assert this record, and when.
references (6)
External citations — patches, advisories, analysis.
- https://github.com/louislam/uptime-kuma/commit/f28dccf4e11f041564293e4f407e69ab9ee2277fcnnvd
- https://github.com/louislam/uptime-kuma/security/advisories/GHSA-v4v2-8h88-65qjcnnvd
- https://github.com/louislam/uptime-kuma/commit/f28dccf4e11f041564293e4f407e69ab9ee2277fenisa_euvd
- https://github.com/louislam/uptime-kuma/security/advisories/GHSA-v4v2-8h88-65qjenisa_euvd
- https://github.com/louislam/uptime-kuma/commit/f28dccf4e11f041564293e4f407e69ab9ee2277fPatchnvd
- https://github.com/louislam/uptime-kuma/security/advisories/GHSA-v4v2-8h88-65qjExploitVendor Advisorynvd
Attackers weaponise vulnerabilities like this against internet-exposed services. See what is exposed on your perimeter with a free passive scan.
Free scan