CVE-2024-29196
lowPriorität · verfolgen · 11EPSS 0.006 · 48. PerzentilEUUSEPSS · bewertet 2026-10-27
phpMyFAQ is an open source FAQ web application for PHP 8.1+ and MySQL, PostgreSQL and other databases. There is a Path Traversal vulnerability in Attachments that allows attackers with admin rights to upload malicious files to other locations of the web root. This vulnerability is fixed in 3.2.6.
cvss
Technischer Schweregrad, 0–10. Eine Zeile je Quelle.
Basiswert 0–10 · höher = schwerwiegender · Vektor überfahren zum Auflösen
SSVC
Eine Handlungsentscheidung — aus Ausnutzung und Auswirkung.
schwächen
Die CWE-Schwächeklassen, zu denen dies gehört.
betroffene Produkte (4)
Betroffene Produkte und Versionsbereiche.
Advisories (1)
Hersteller- und Ökosystem-Meldungen dazu.
- GHSA-mmh6-5cpf-2c72phpMyFAQ Path Traversal in Attachments2024-03-25ghsa · osvUS
### Summary There is a Path Traversal vulnerability in Attachments that allows attackers with admin rights to upload malicious files to other locations of the web root. ### PoC 1. In settings, the attachment location is vulnerable to path traversal and can be set to e.g ..\hacked 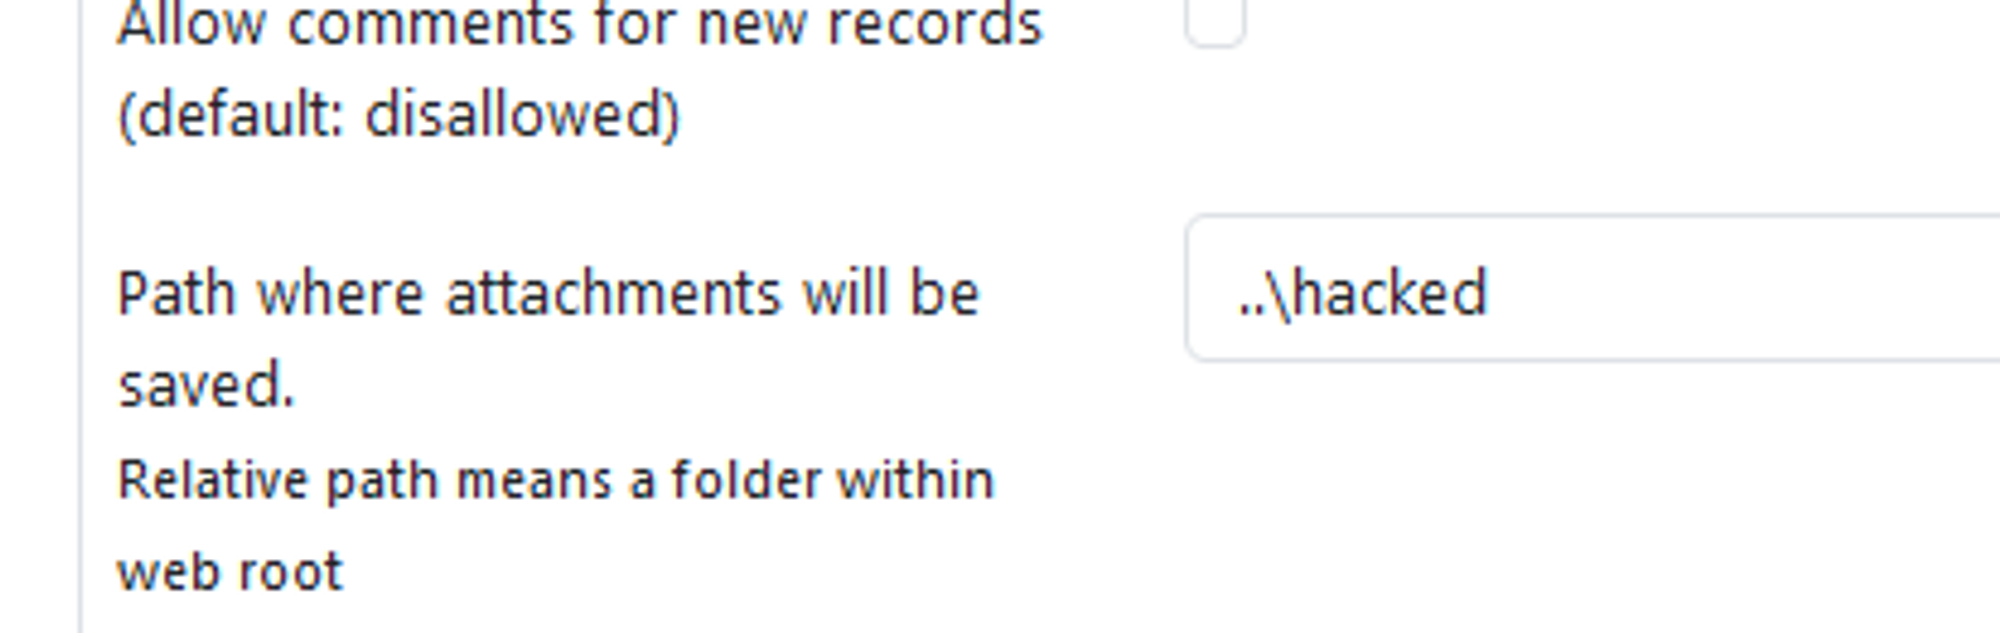 2. When the above is set, attachments files are now uploaded to e.g C:\Apps\XAMPP\htdocs\hacked instead of C:\Apps\XAMPP\htdocs\phpmyfaq\attachments 3. Verify this by uploading an attachment and see that the "hacked" directory is now created in the web root folder with the attachment file inside. 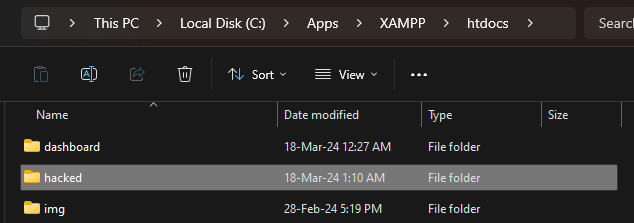 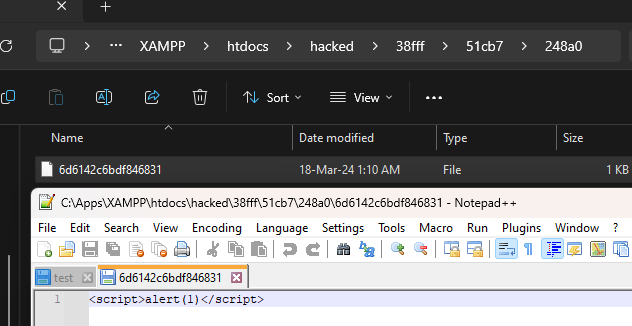 ### Impact Attackers can potentially upload malicious files outside the specified directory.
auch bekannt als (3)
Weitere Namen und Kennungen dieser Entität.
quellen
Welche Quellen diesen Datensatz belegen und wann.
Referenzen (7)
Externe Belege — Patches, Meldungen, Analysen.
- https://cxsecurity.com/cveshow/CVE-2024-29196/cnnvd
- https://github.com/thorsten/phpMyFAQ/commit/7ae2559f079cd5fc9948b6fdfb87581f93840f62cnnvd
- https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-mmh6-5cpf-2c72cnnvd
- https://github.com/thorsten/phpMyFAQ/commit/7ae2559f079cd5fc9948b6fdfb87581f93840f62enisa_euvd
- https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-mmh6-5cpf-2c72enisa_euvd
- https://github.com/thorsten/phpMyFAQ/commit/7ae2559f079cd5fc9948b6fdfb87581f93840f62Patchnvd
- https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-mmh6-5cpf-2c72ExploitVendor Advisorynvd
Angreifer nutzen Schwachstellen wie diese gegen im Internet exponierte Dienste aus. Sehen Sie mit einem kostenlosen Passiv-Scan, was exponiert ist.
Kostenloser Scan